How to Create the Local Realm in Keycloak
This guide shows you how to create the local realm in Keycloak, the realm users sign up through and the one the first user of every tenant is created in.
Type |
How-to guide |
Goal |
Give a Keycloak installation the |
Audience |
Platform Operator with admin access to Keycloak. |
When to use |
Use this guide once per Keycloak installation, after the governance components are running and before the first user signs up. |
Prerequisites
Confirm the following before you begin.
Access and permissions required
You need the following access and permissions:
-
The Keycloak
admincredentials for the Administration Console.
Tools and versions required
You need the following tools:
-
A browser that reaches the Keycloak Administration Console at
<keycloak.host>/auth.
Resources that must exist before starting
The following must already exist:
-
A running Keycloak, deployed with the governance components. See Install Axual Governance.
-
The Self-Service hostname, which the client’s
Root URLand the login URL are built from.
Replace every <…> placeholder with your own value before opening a URL.
|
Local users and SSO users
The Axual Platform supports two types of users, and each type logs in through its own realm:
-
Local Users: users who sign up directly with Google or an email address. They log in through the
localrealm this guide creates. -
SSO Users: users who come from the customer’s own identity system, such as Azure AD or Lightweight Directory Access Protocol (LDAP), and reach the platform through a dedicated URL. They skip the sign-up stage and log in through a per-tenant realm, which How to Create an SSO Realm in Keycloak covers.
Before SSO users can log in, a local user must configure SSO settings for their Organization, so the local realm comes first on any installation.
Create the local realm
The realm needs the Self-Service client and the two tenant mappers alongside it, so a signed-up user reaches Self-Service with the tenant they belong to.
-
Access the Keycloak Admin Console (
/auth)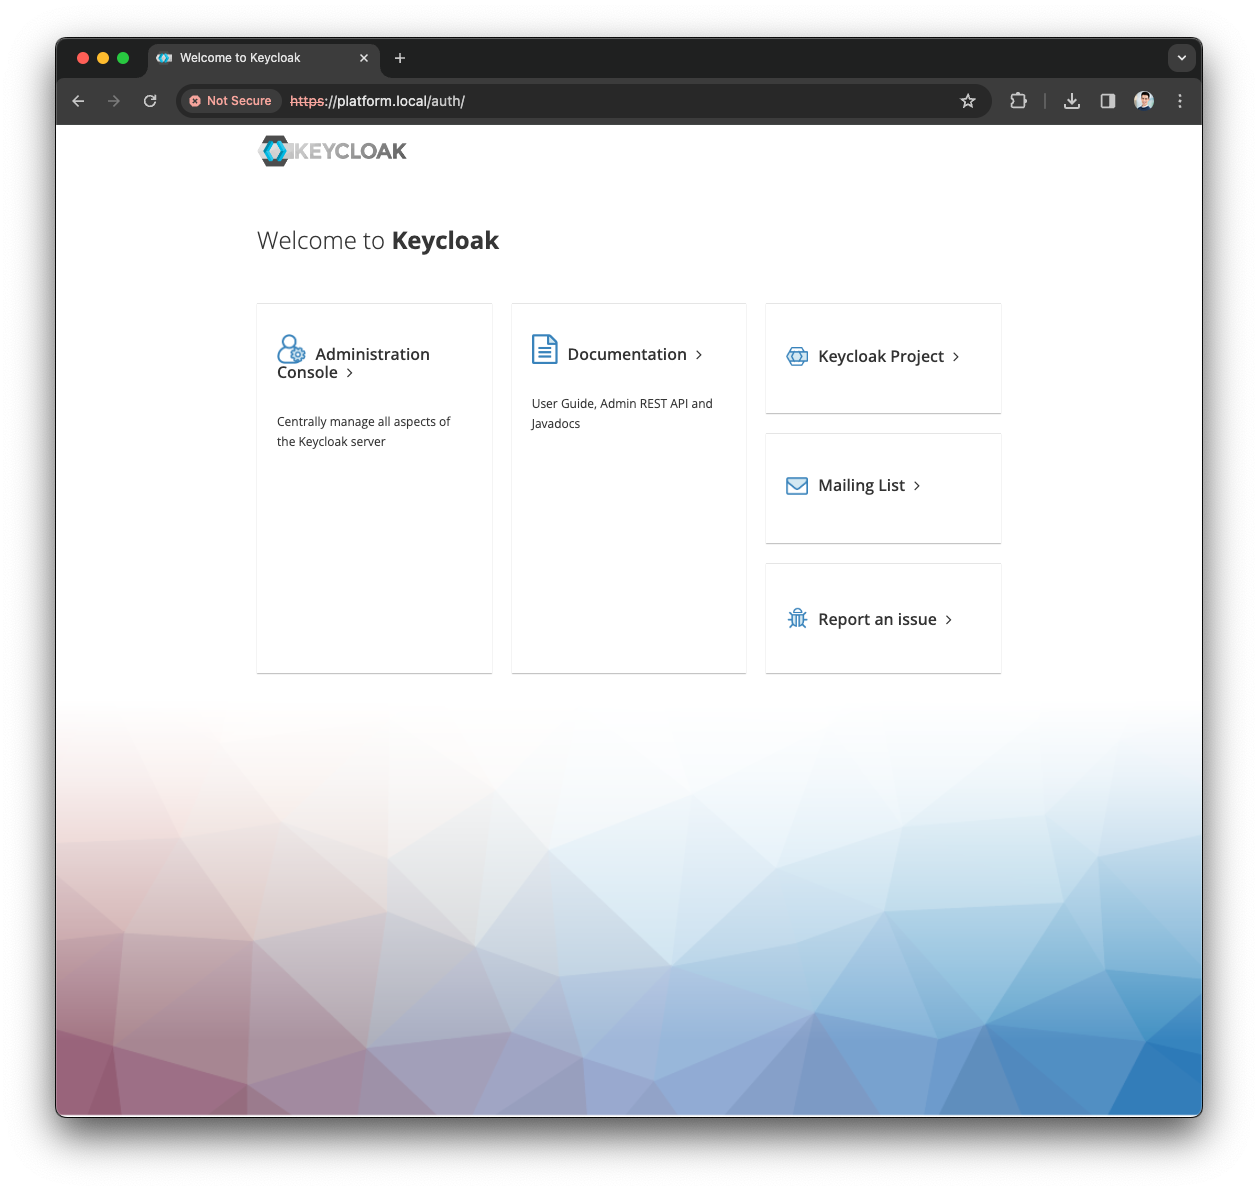
-
Press the
Administration Consoleand provide theadmincredentials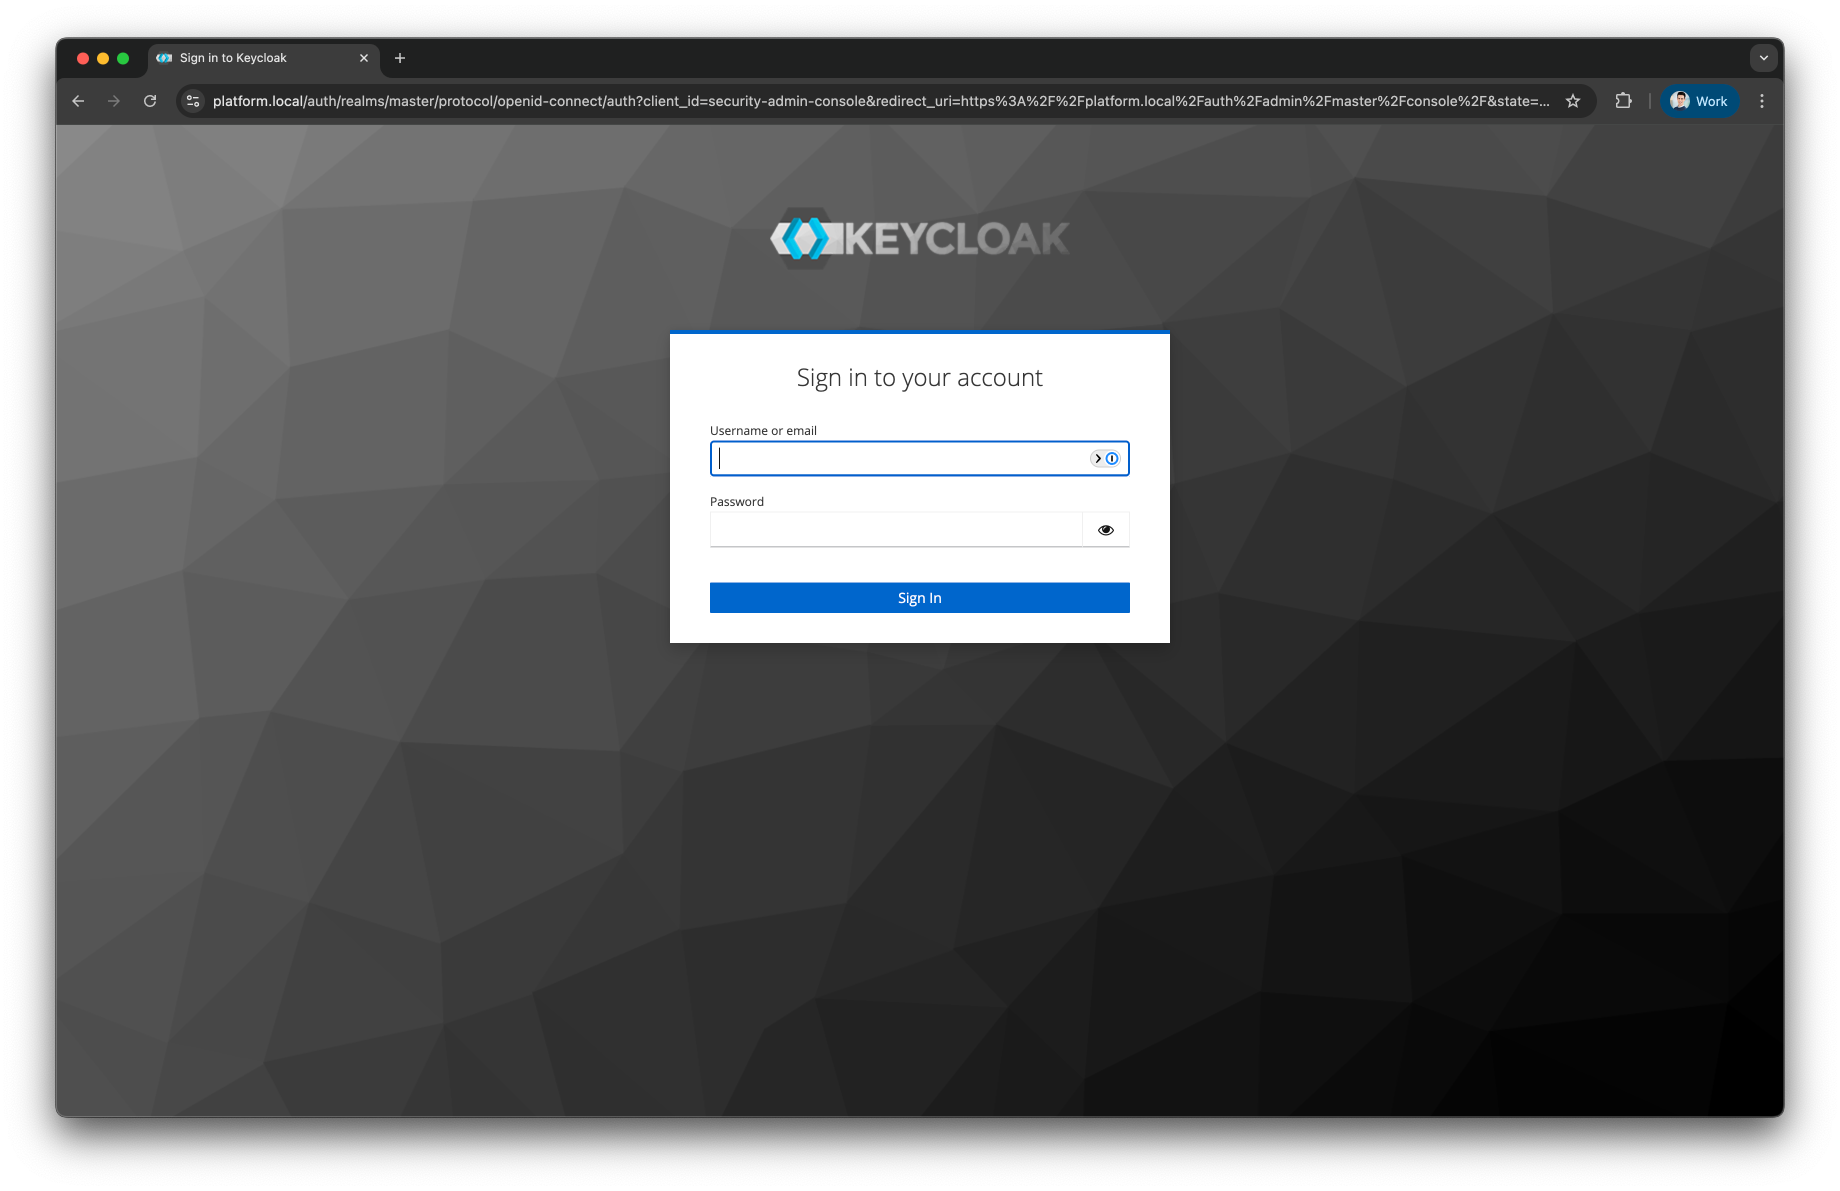
-
Open the Realm dropdown in the top-left corner
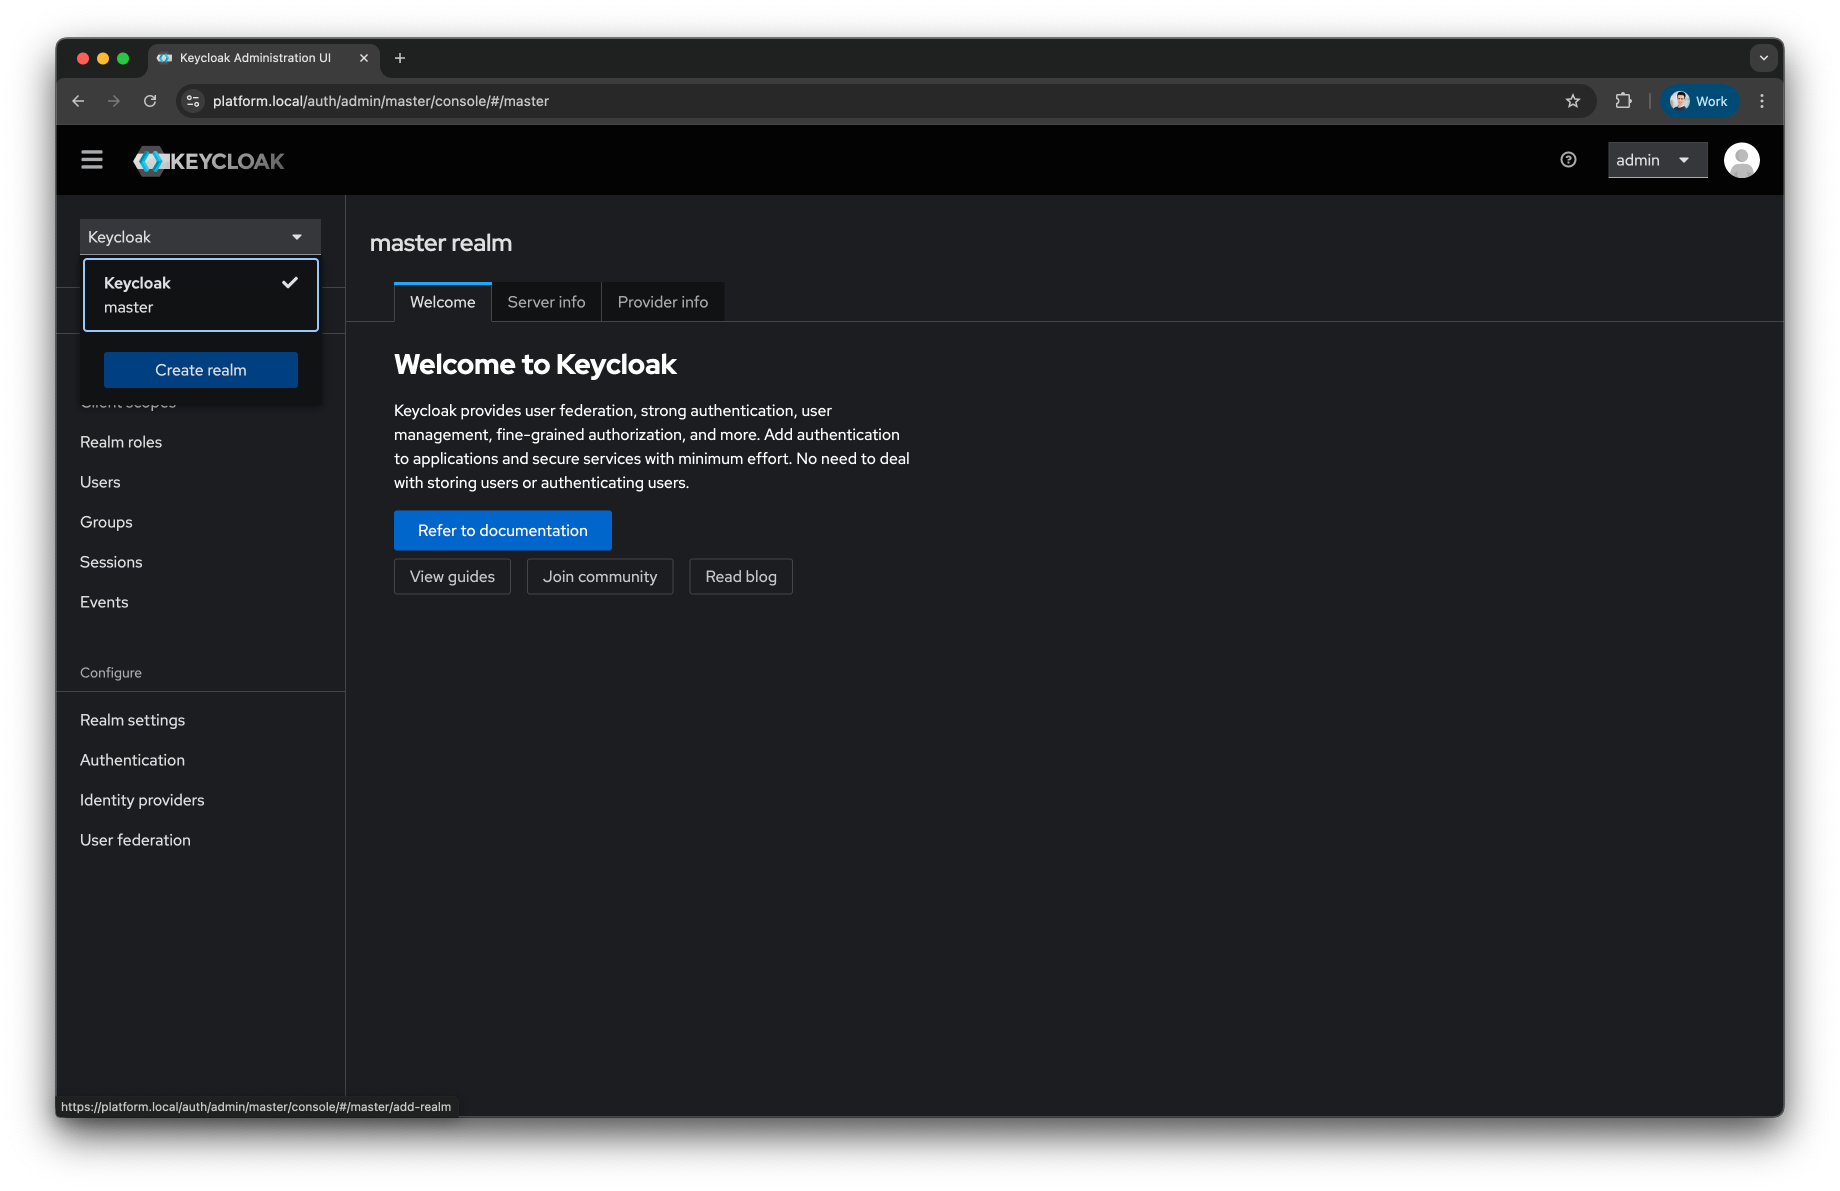
-
Press the
Create Realmbutton -
Fill the
Realm namewith local and press theCreatebutton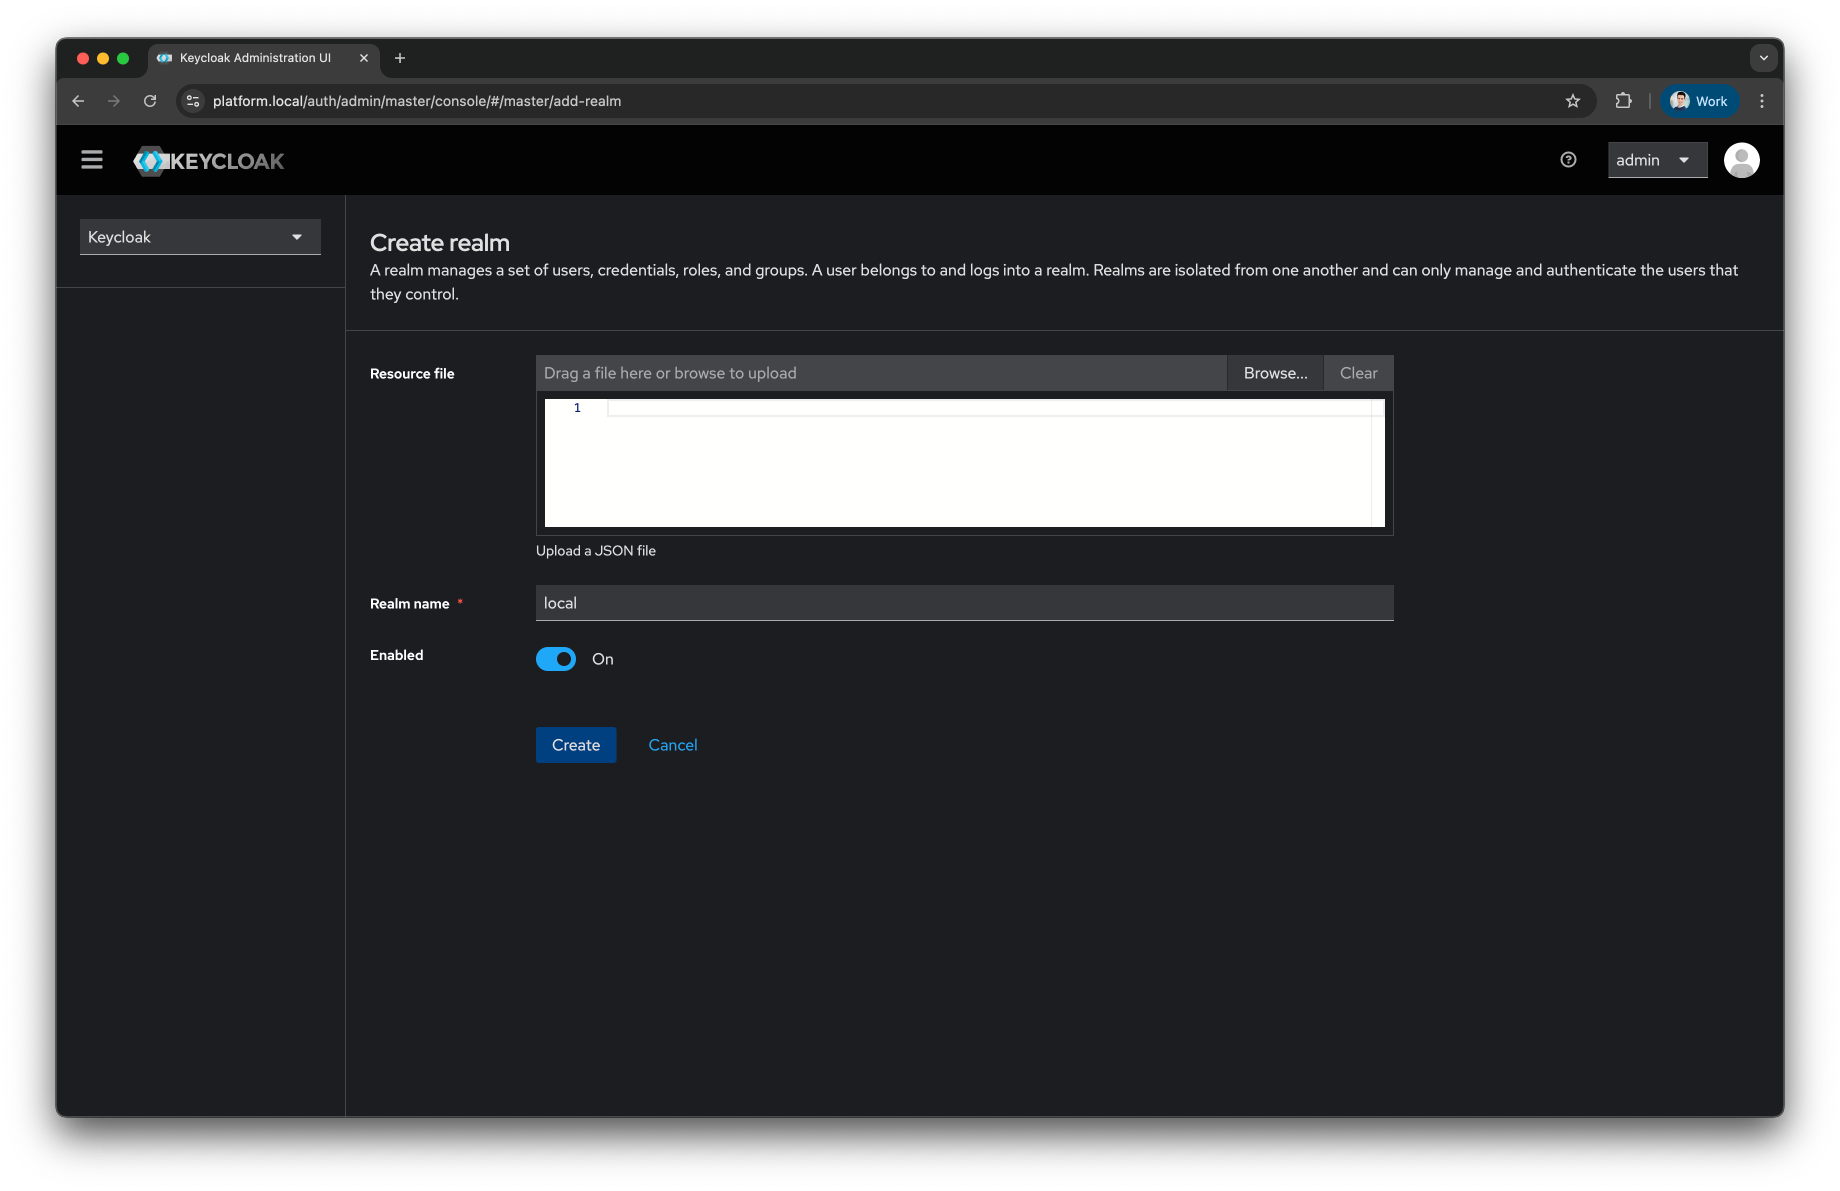
-
Open the Menu and press the
Realm Settingsbutton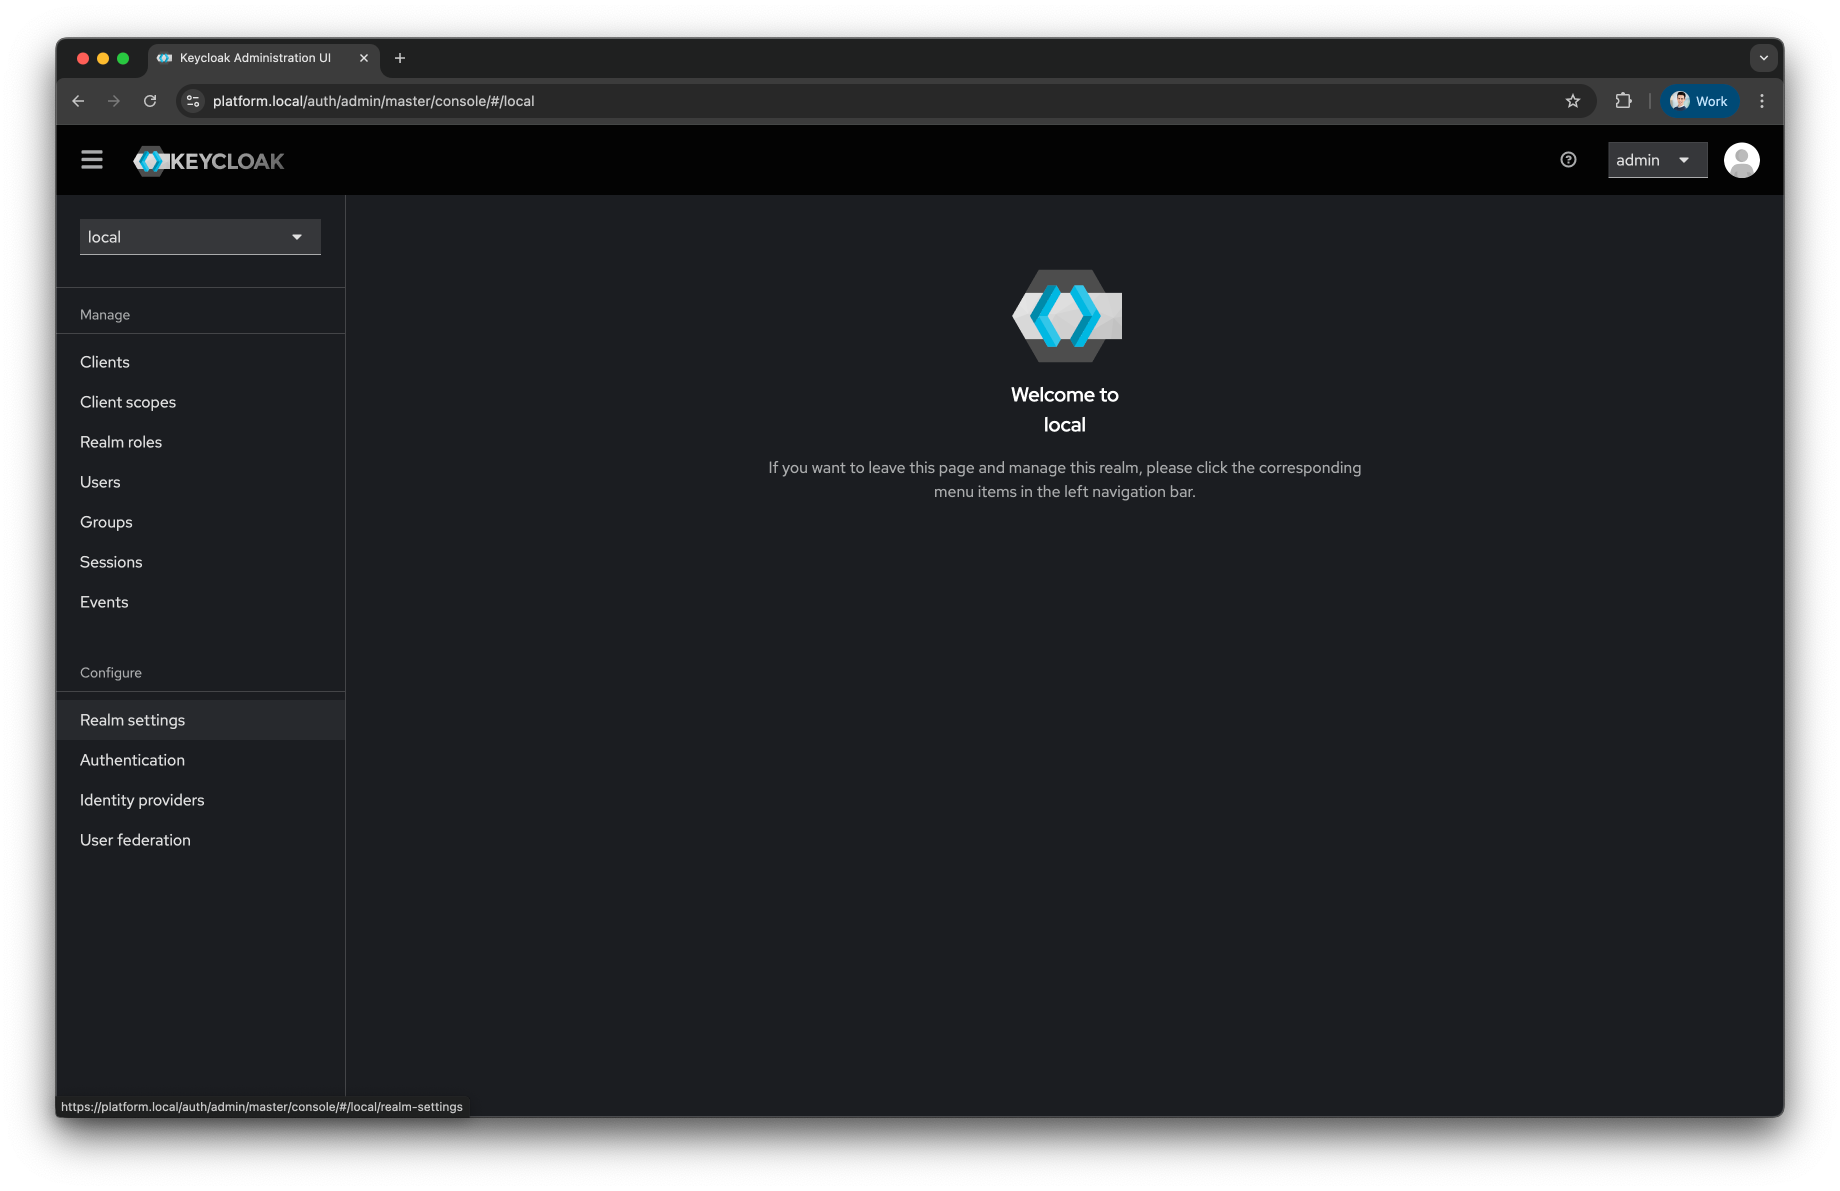
-
In the
Generaltab enable theUser-managed accesstoggle and press theSavebutton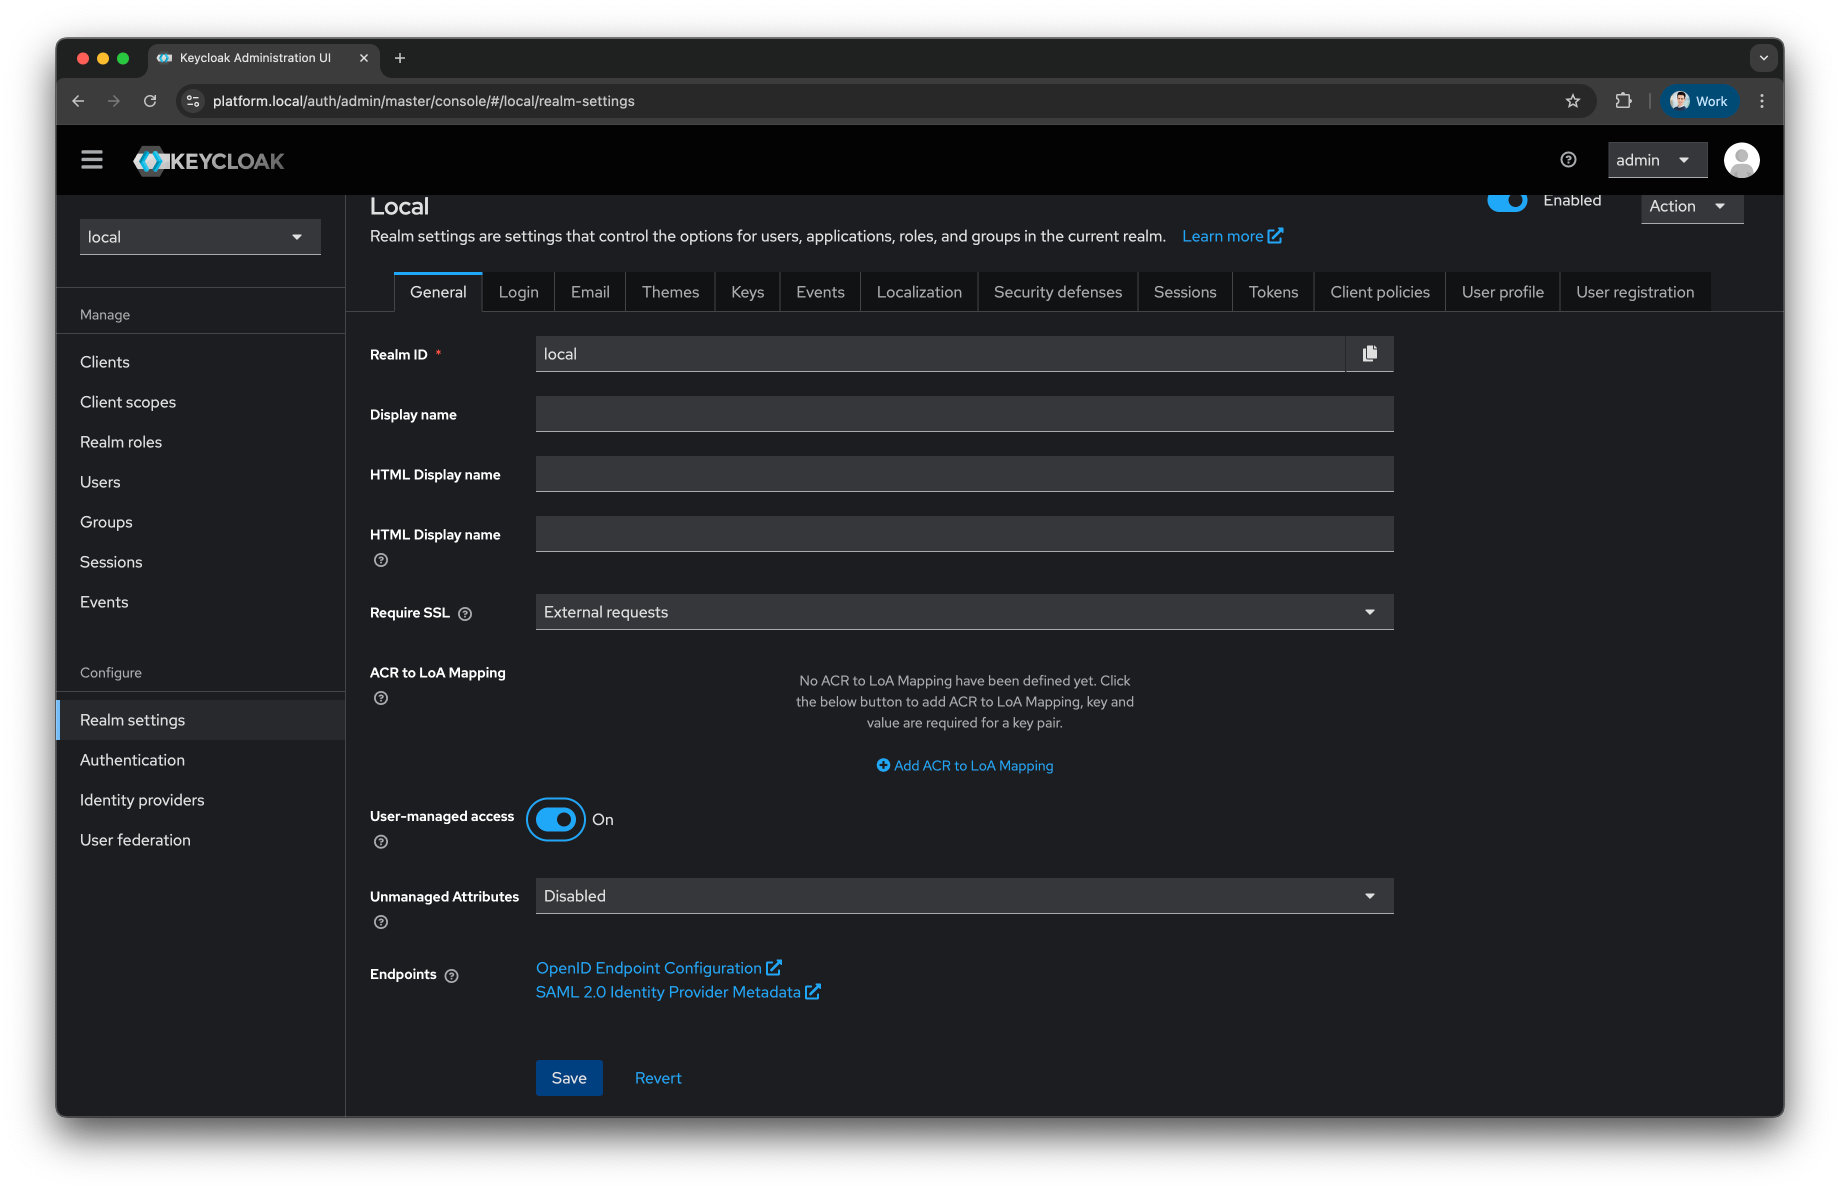
-
In the
Logintab on top and enable theUser registrationtoggle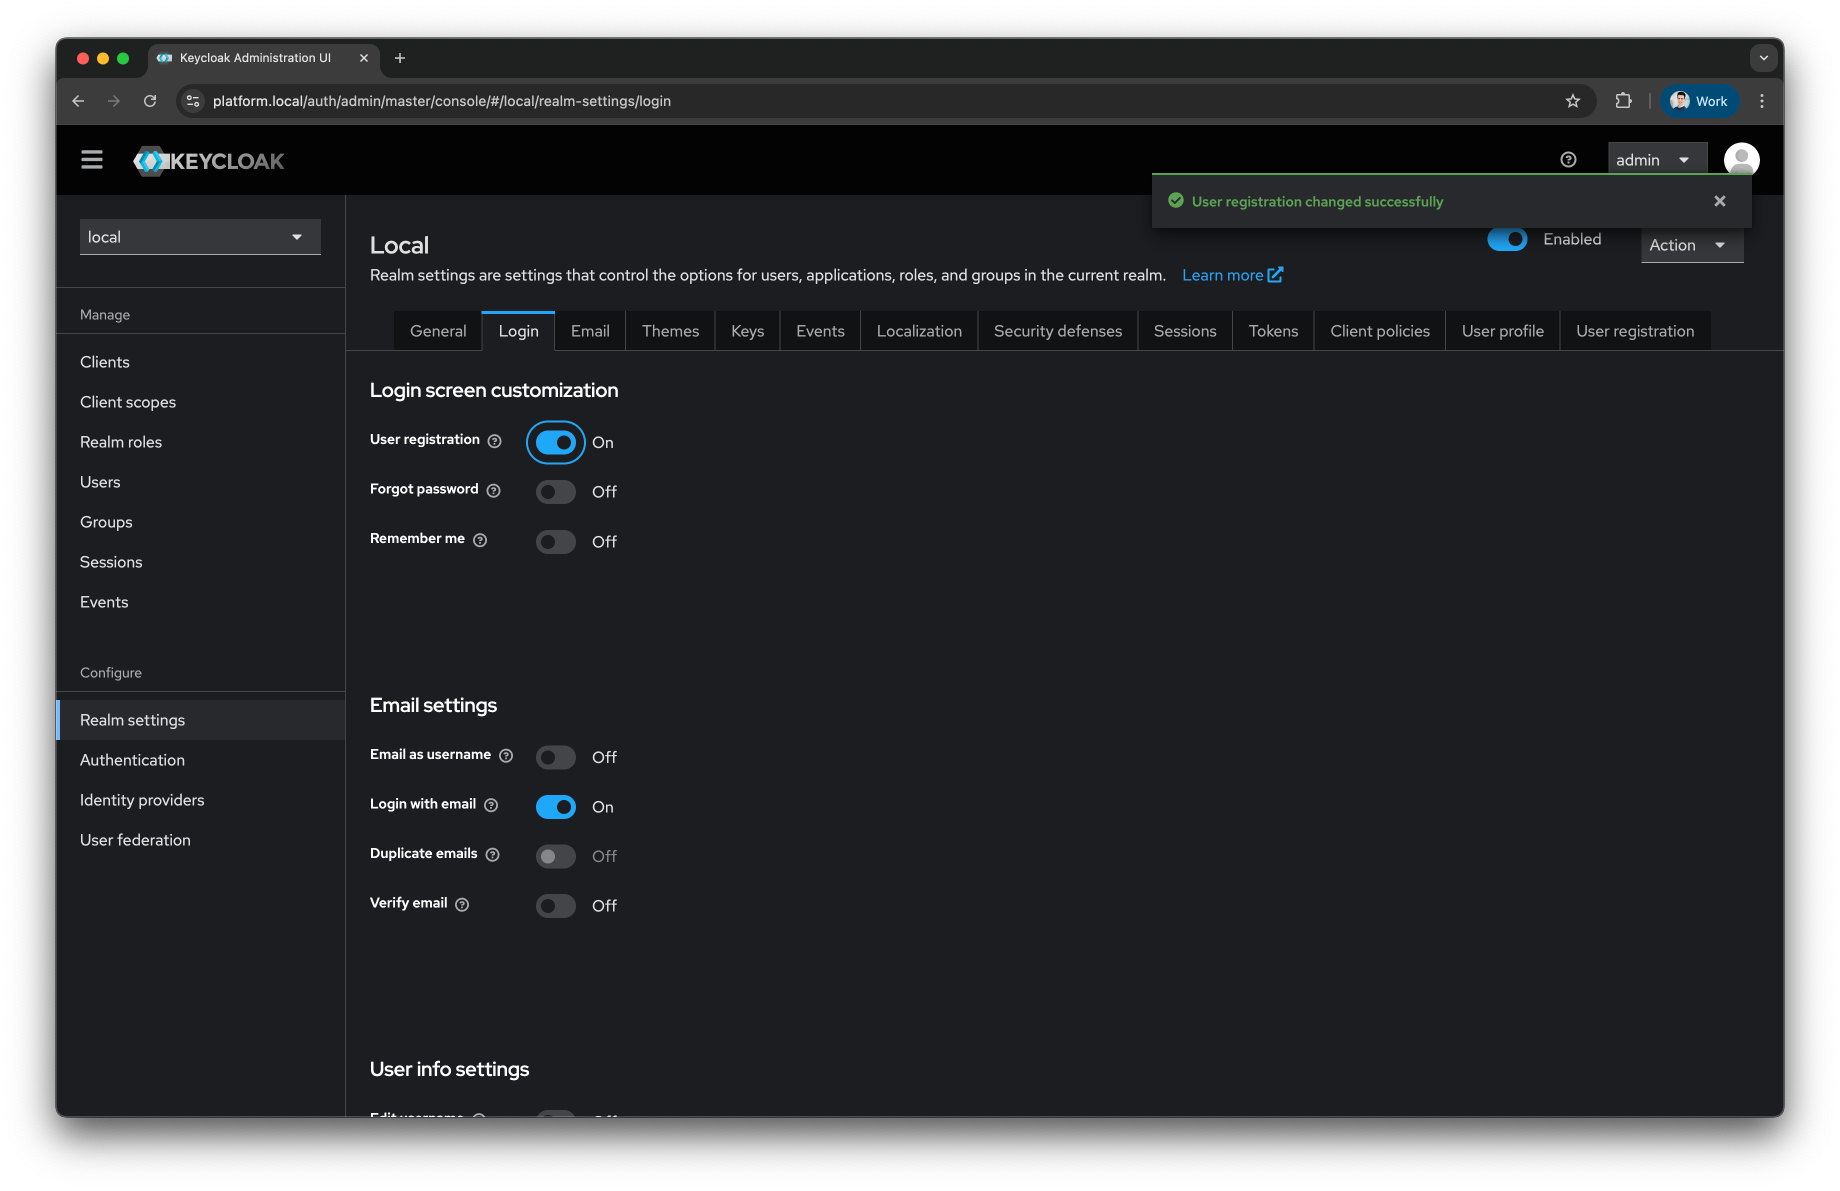
-
Now press the
Clientsmenu -
Press the
Create Clientbutton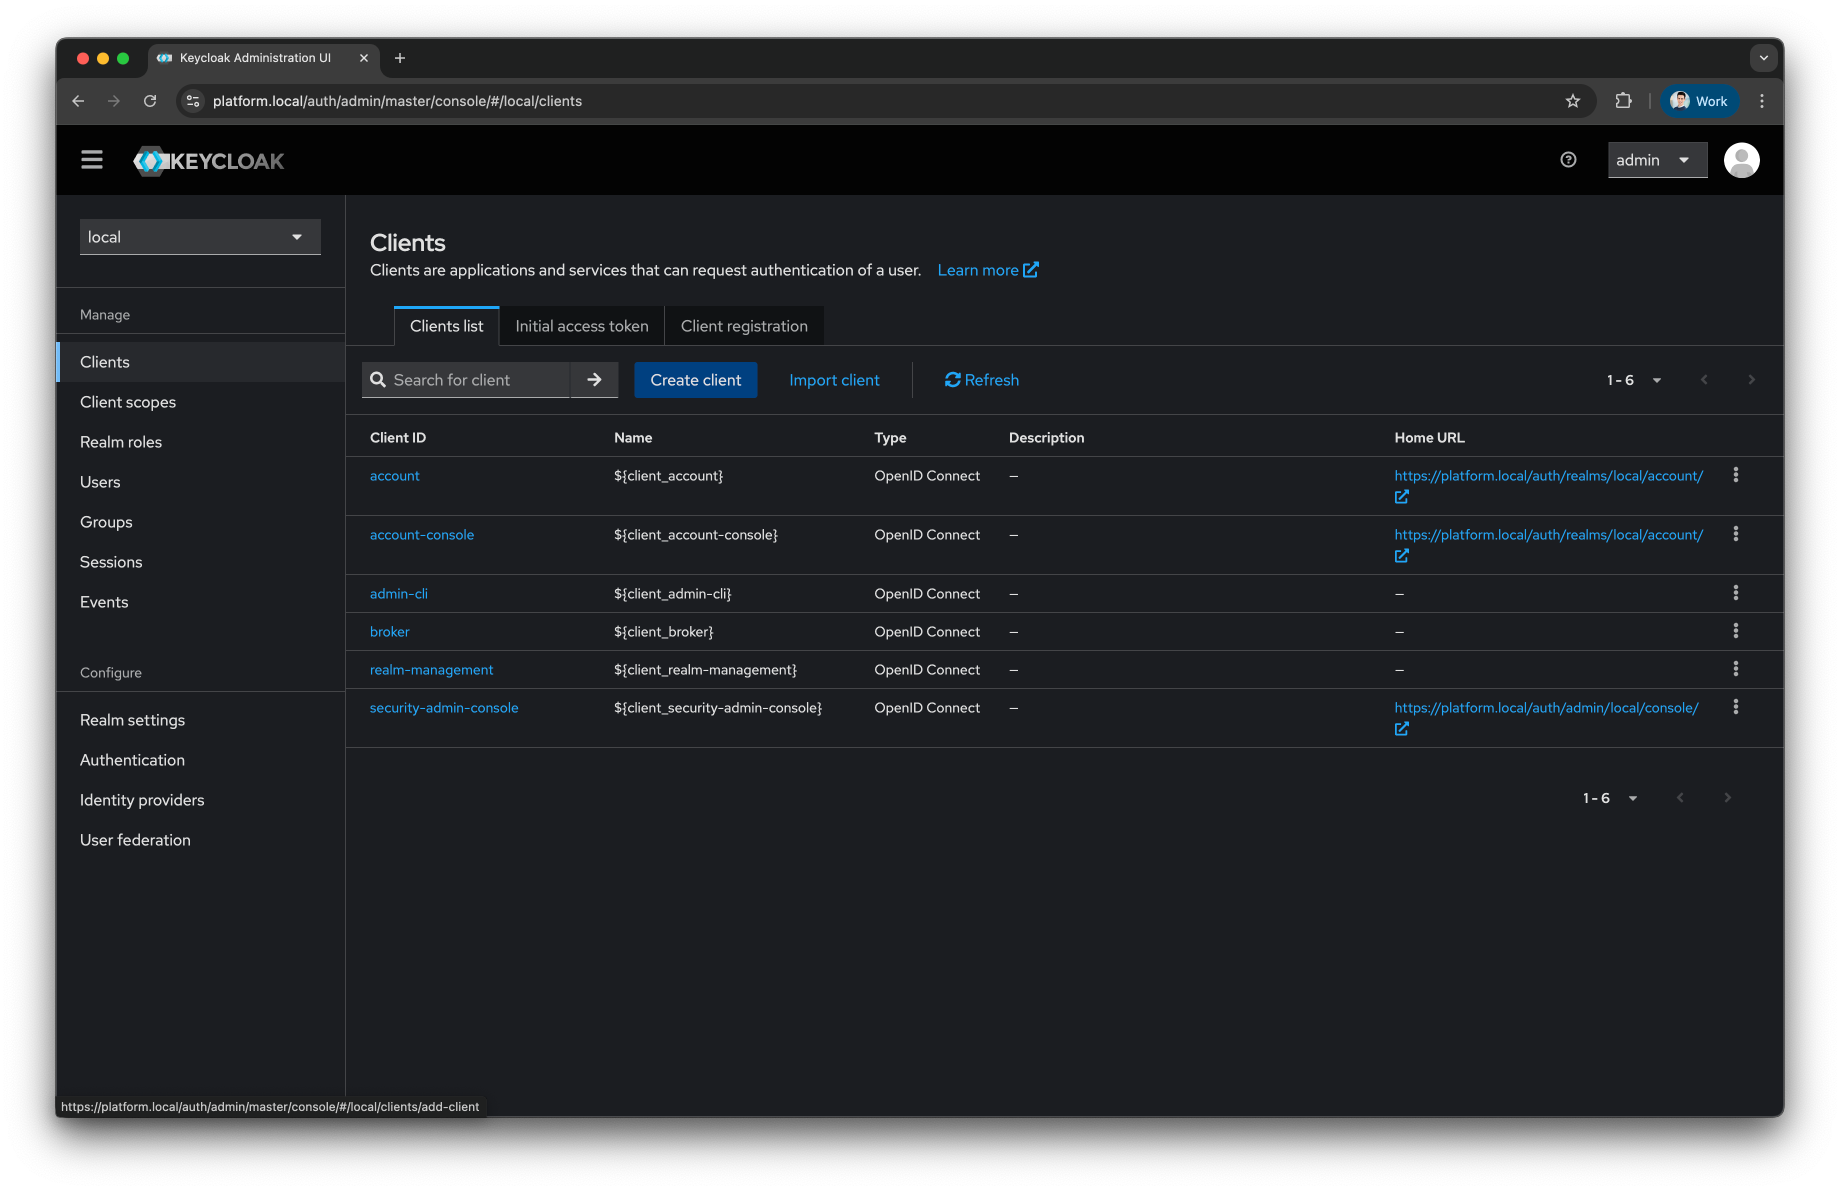
-
Provide the following
General Configuration-
Select OpenID Connect as
Client Type -
Fill the
Client IDasself-service -
Fill the
Nameas Self Service Client -
Provide a meaningful
Descriptionas Client used by the Self-Service to authenticate users
-
-
Press the
Nextbutton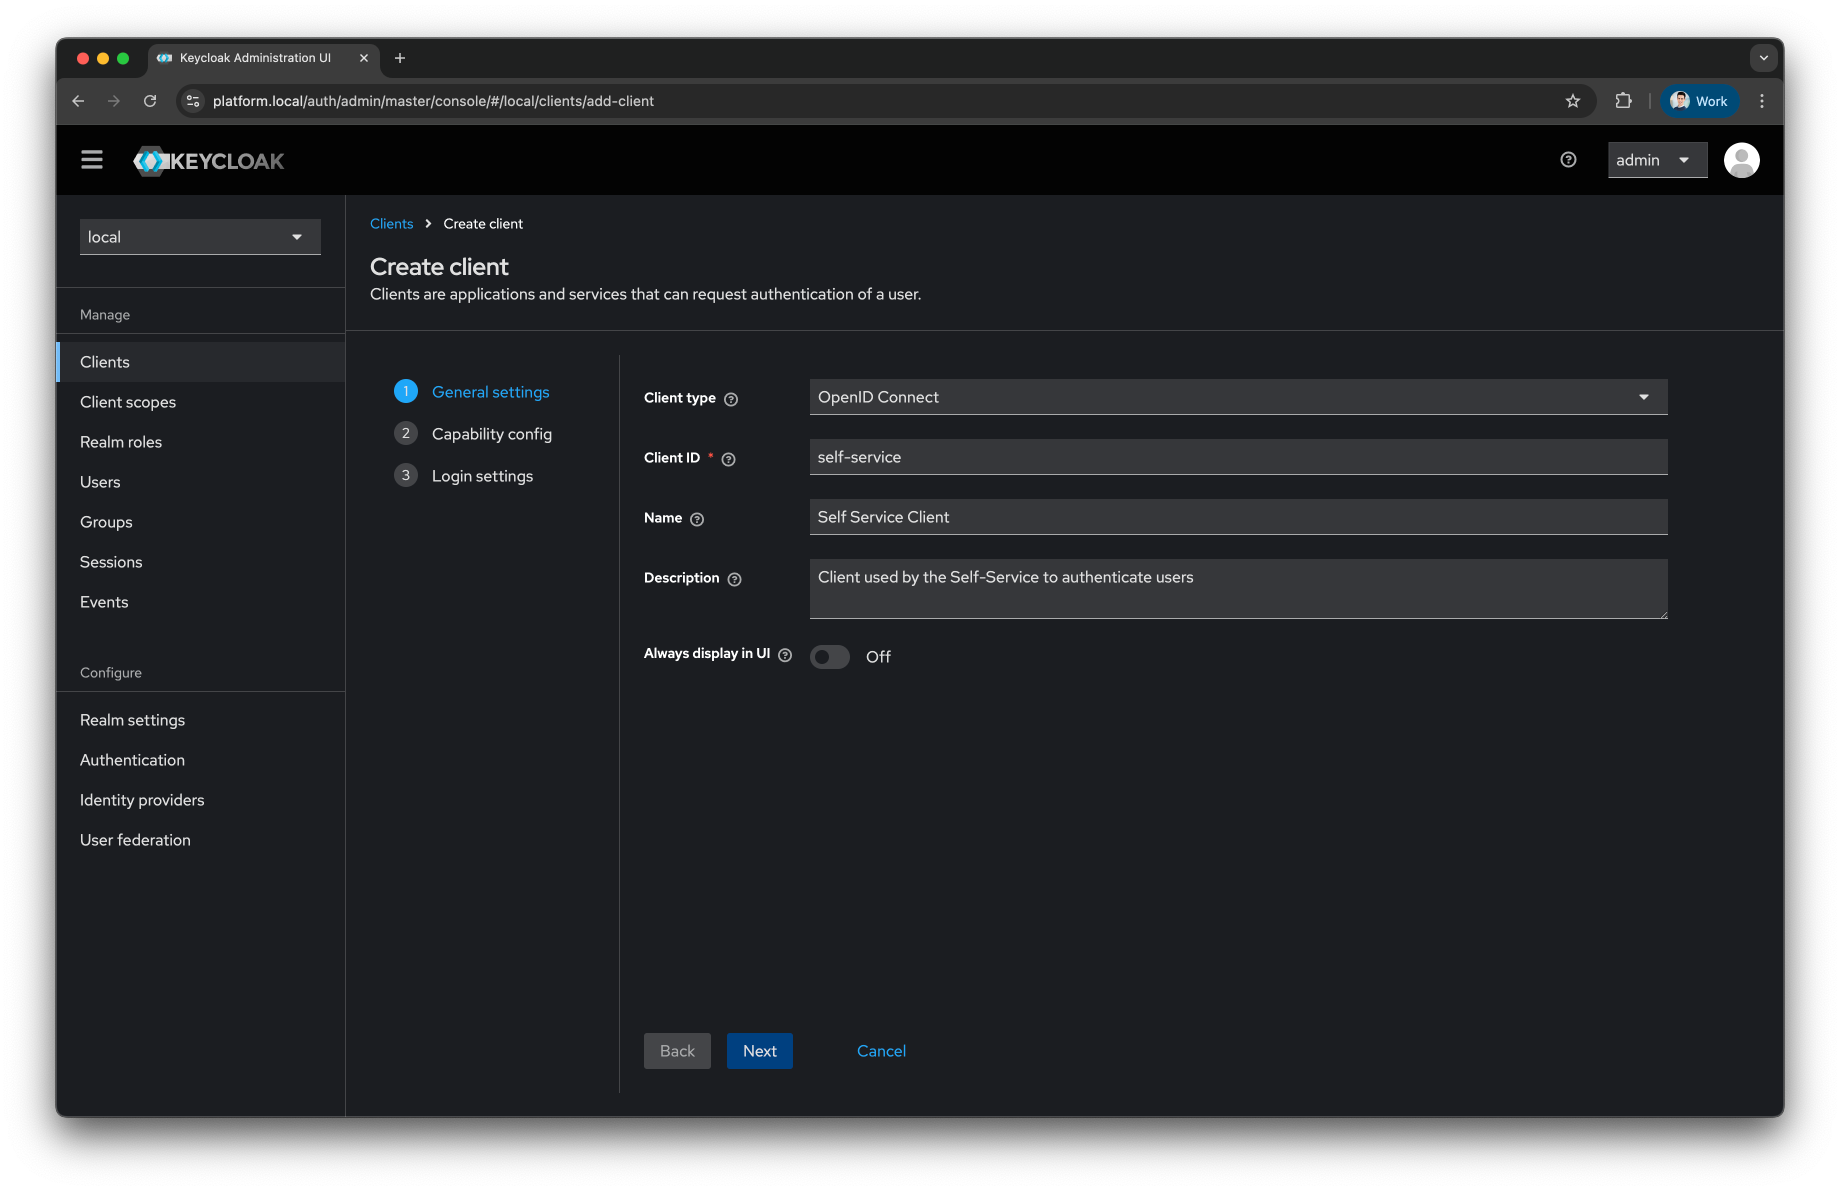
-
Keep the
Capability configas default and press theNextbutton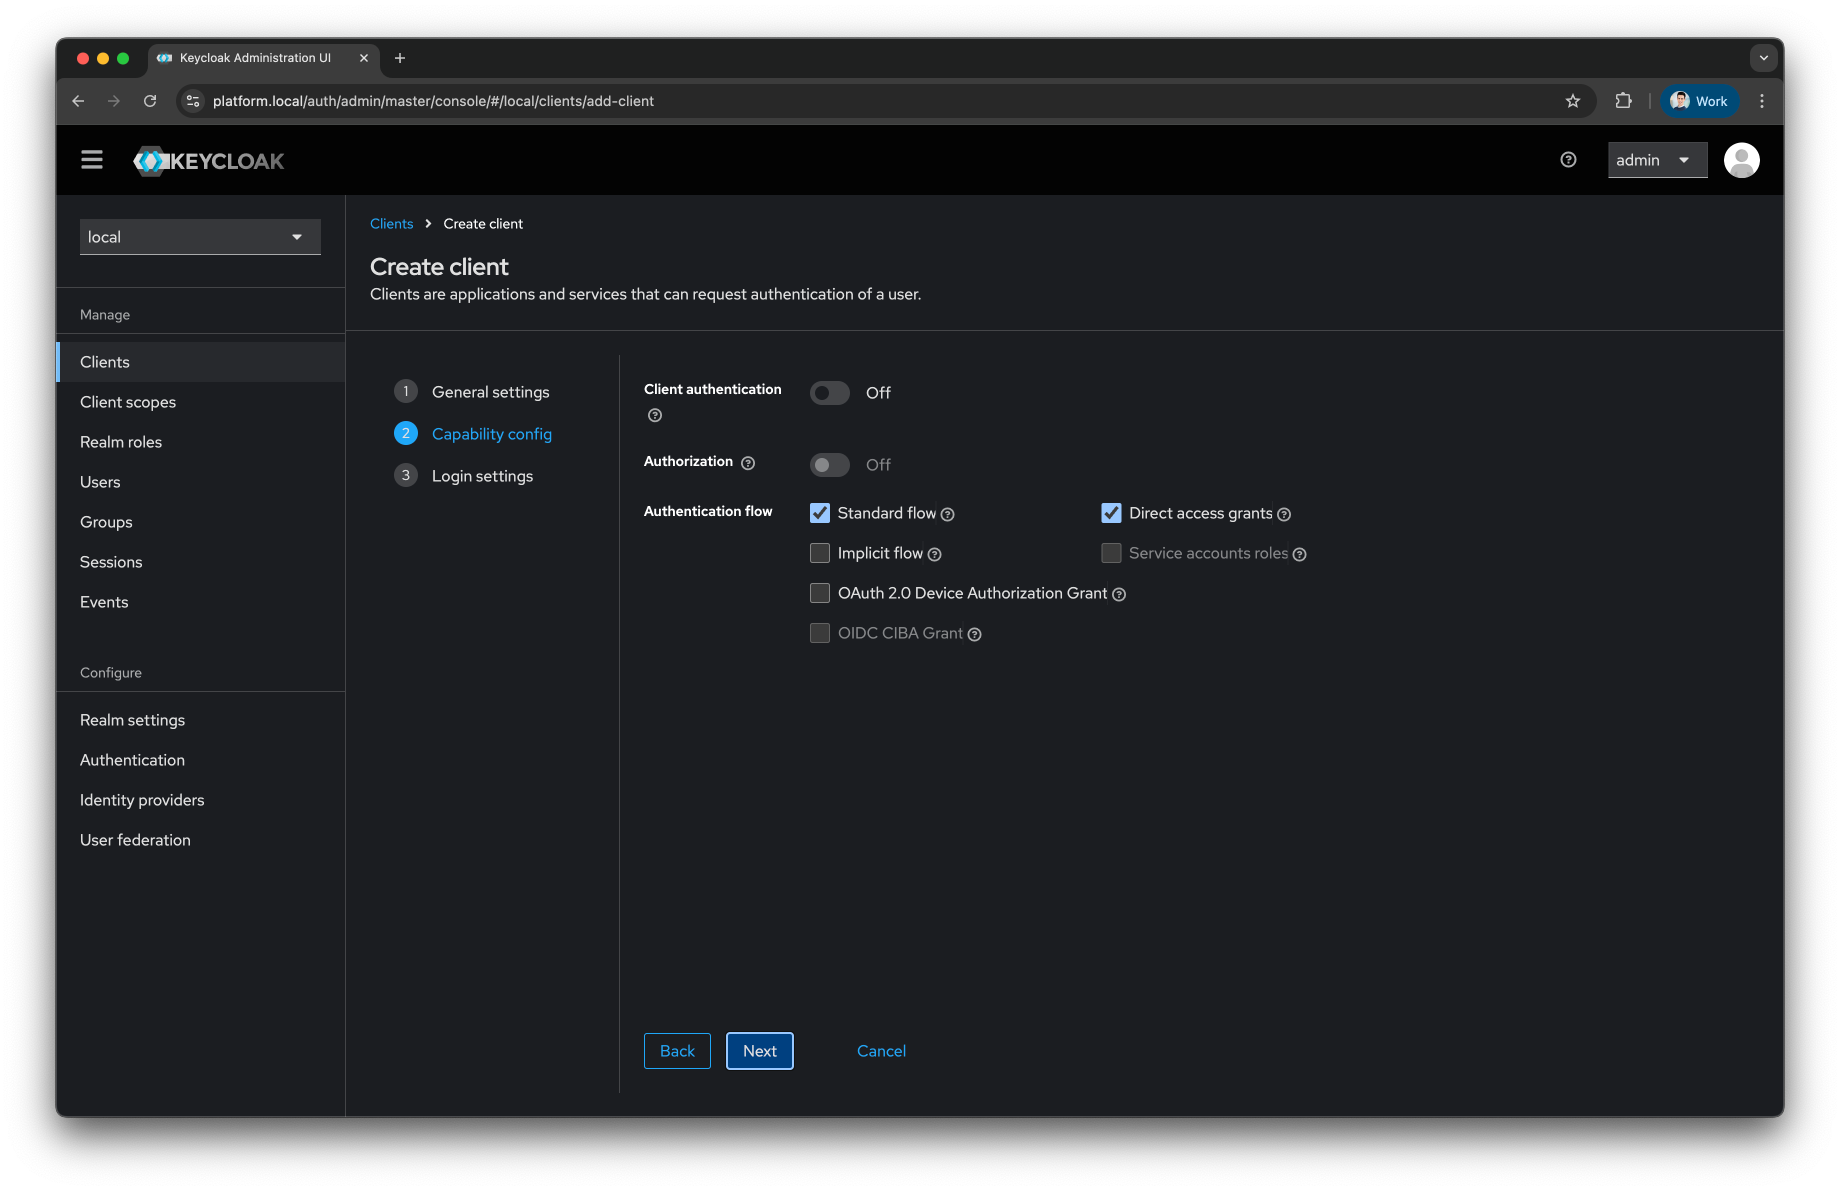
-
In the
Login Settingsprovide the following values-
As
Root URLuse the hostname of your installation, for example https://platform.<domain>/ -
Leave
Home URLempty -
For the
Valid redirect URIs,Valid post logout redirect URIs, andWeb Originsuse the wildcard*The wildcard accepts any redirect target and any browser origin. An attacker who can craft a login link can then have Keycloak send the authorisation code somewhere you do not control. Use the wildcard while you install, then replace all three with the exact Self-Service URLs before the realm serves real users.
-
-
Press the
Savebutton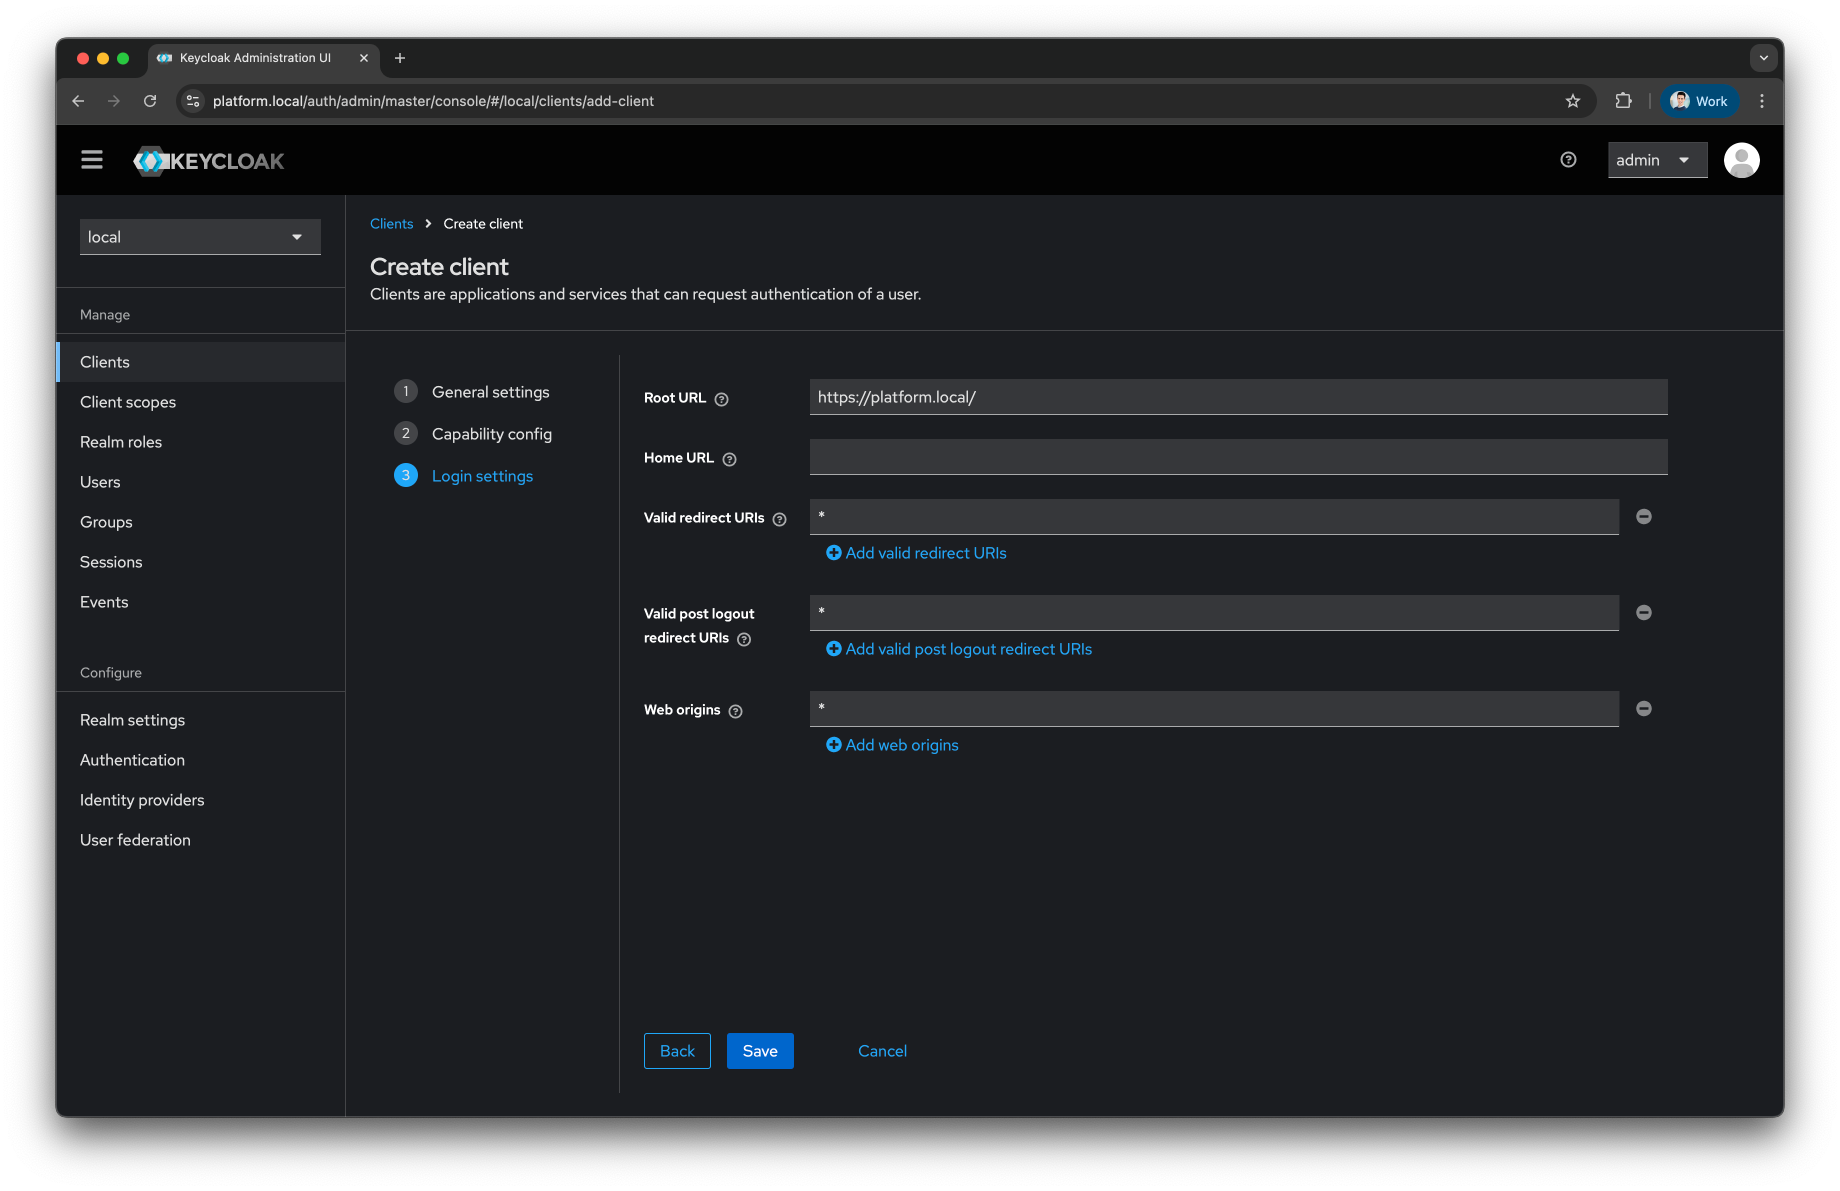
-
Press on the
Client scopestab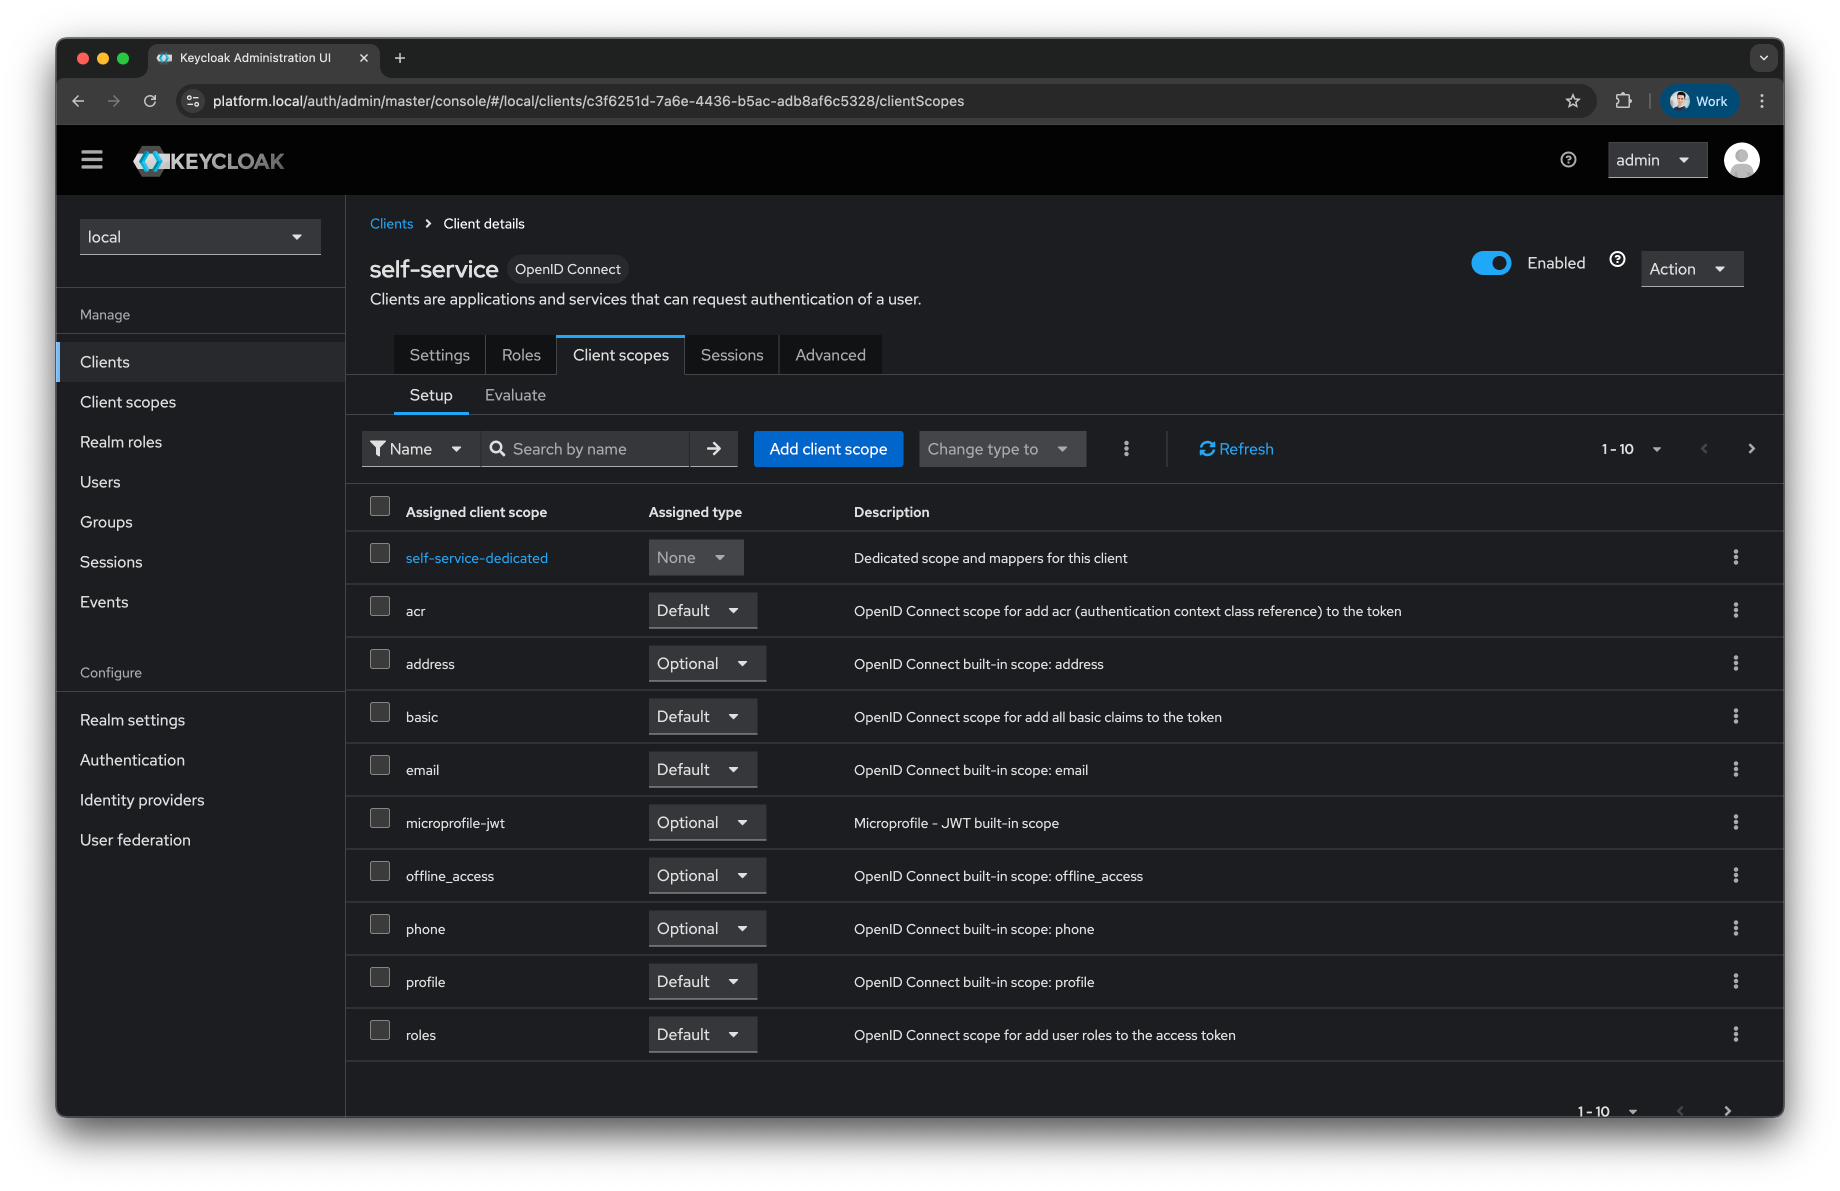
-
Press on the
self-service-dedicatedclient scope -
Select
Configure a new mapper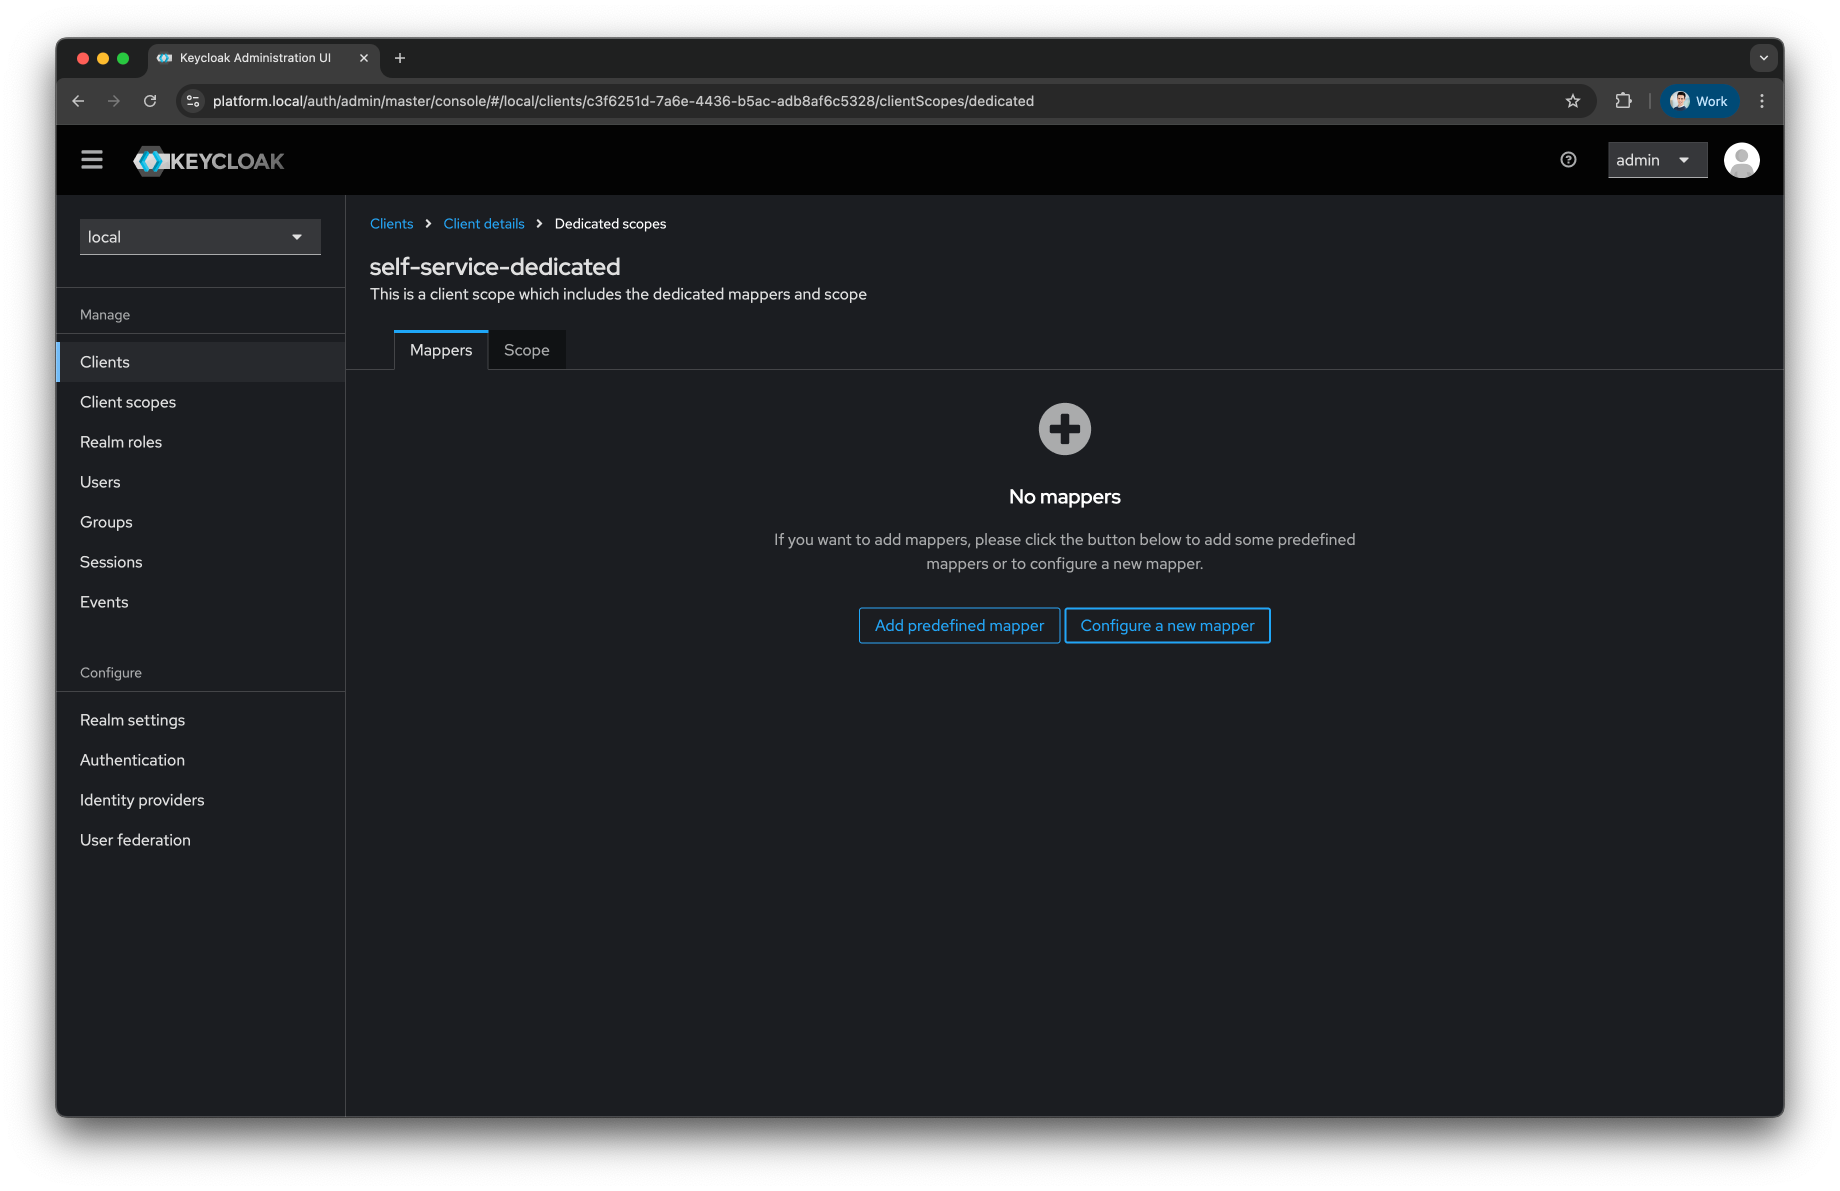
-
Select
User Attribute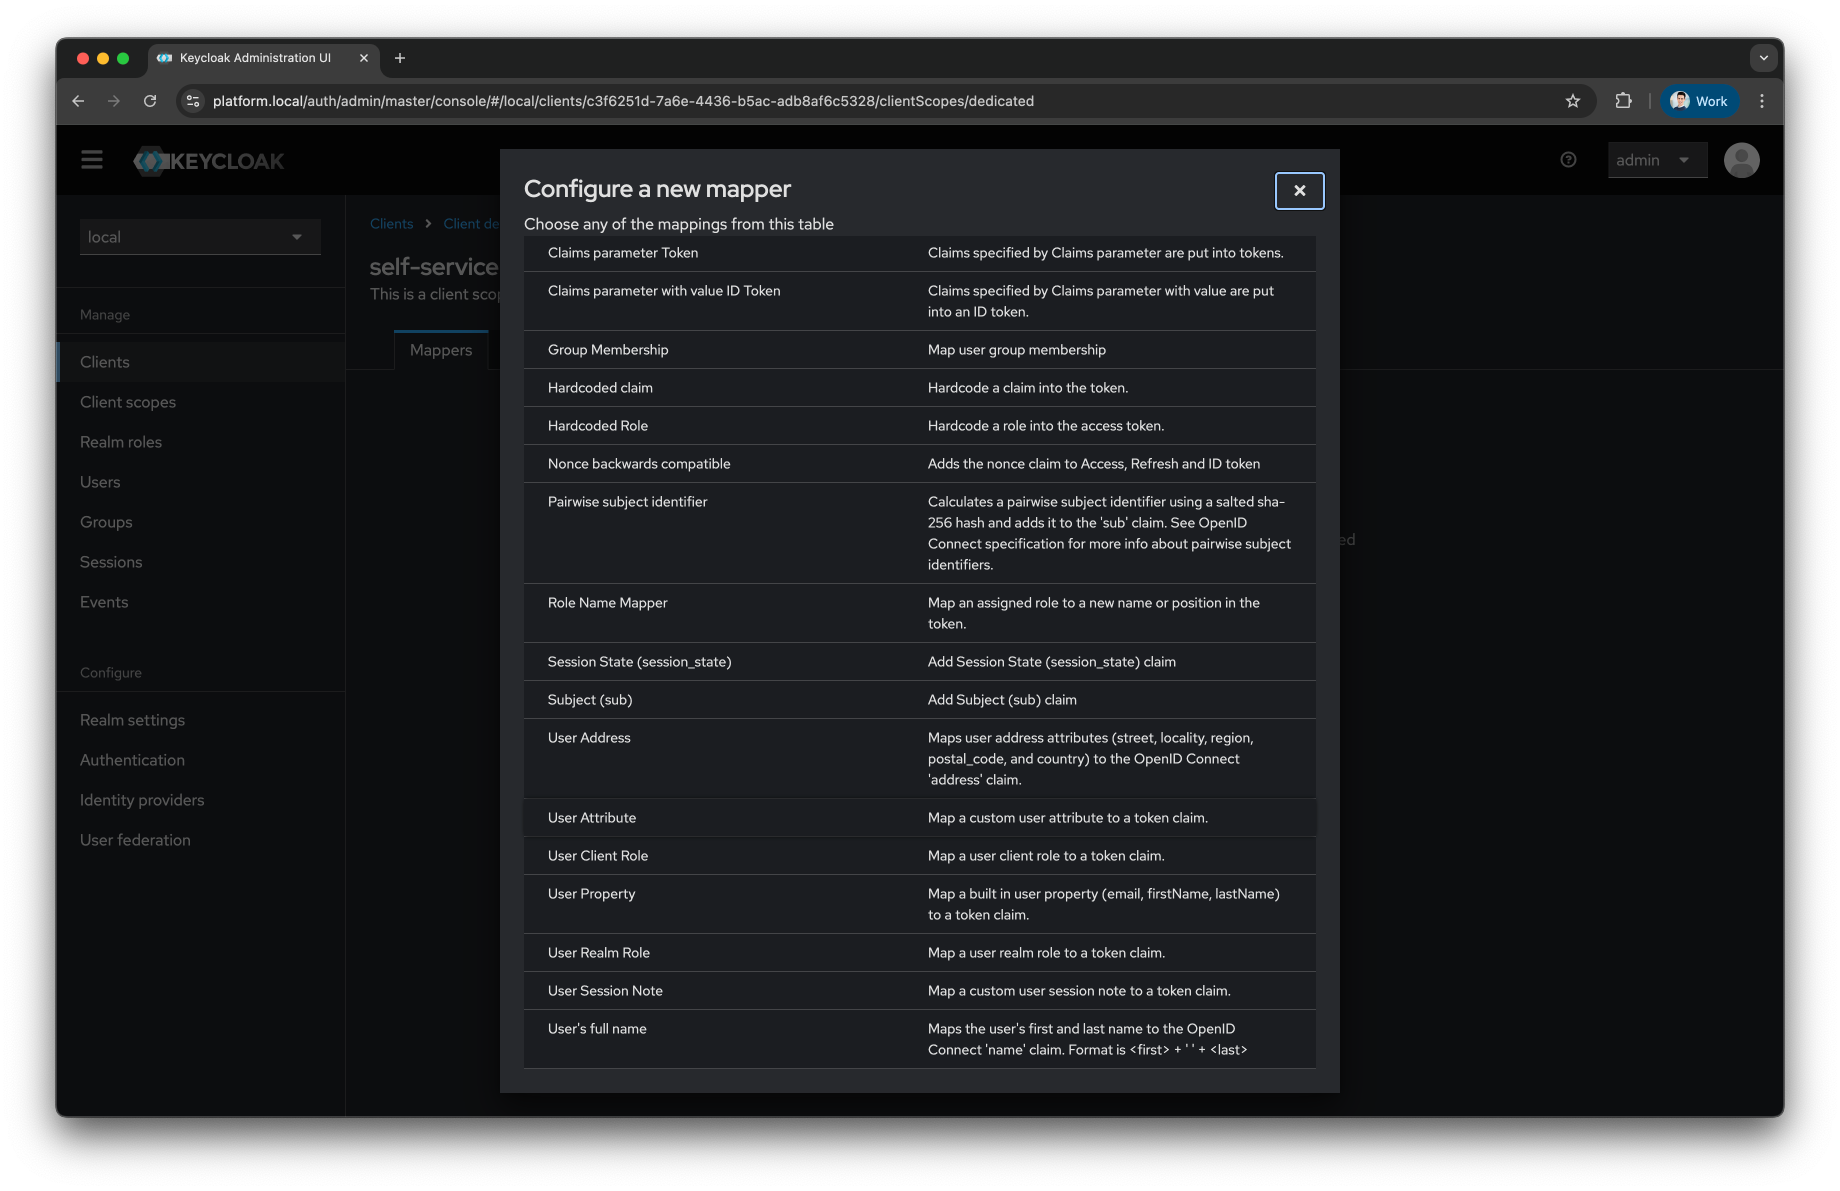
-
Fill the
Nameas Tenant Name Mapper -
Fill the
User Attributeas tenant-name -
Fill the
Token Claim Nameas tenant_name
-
-
Press
Savebutton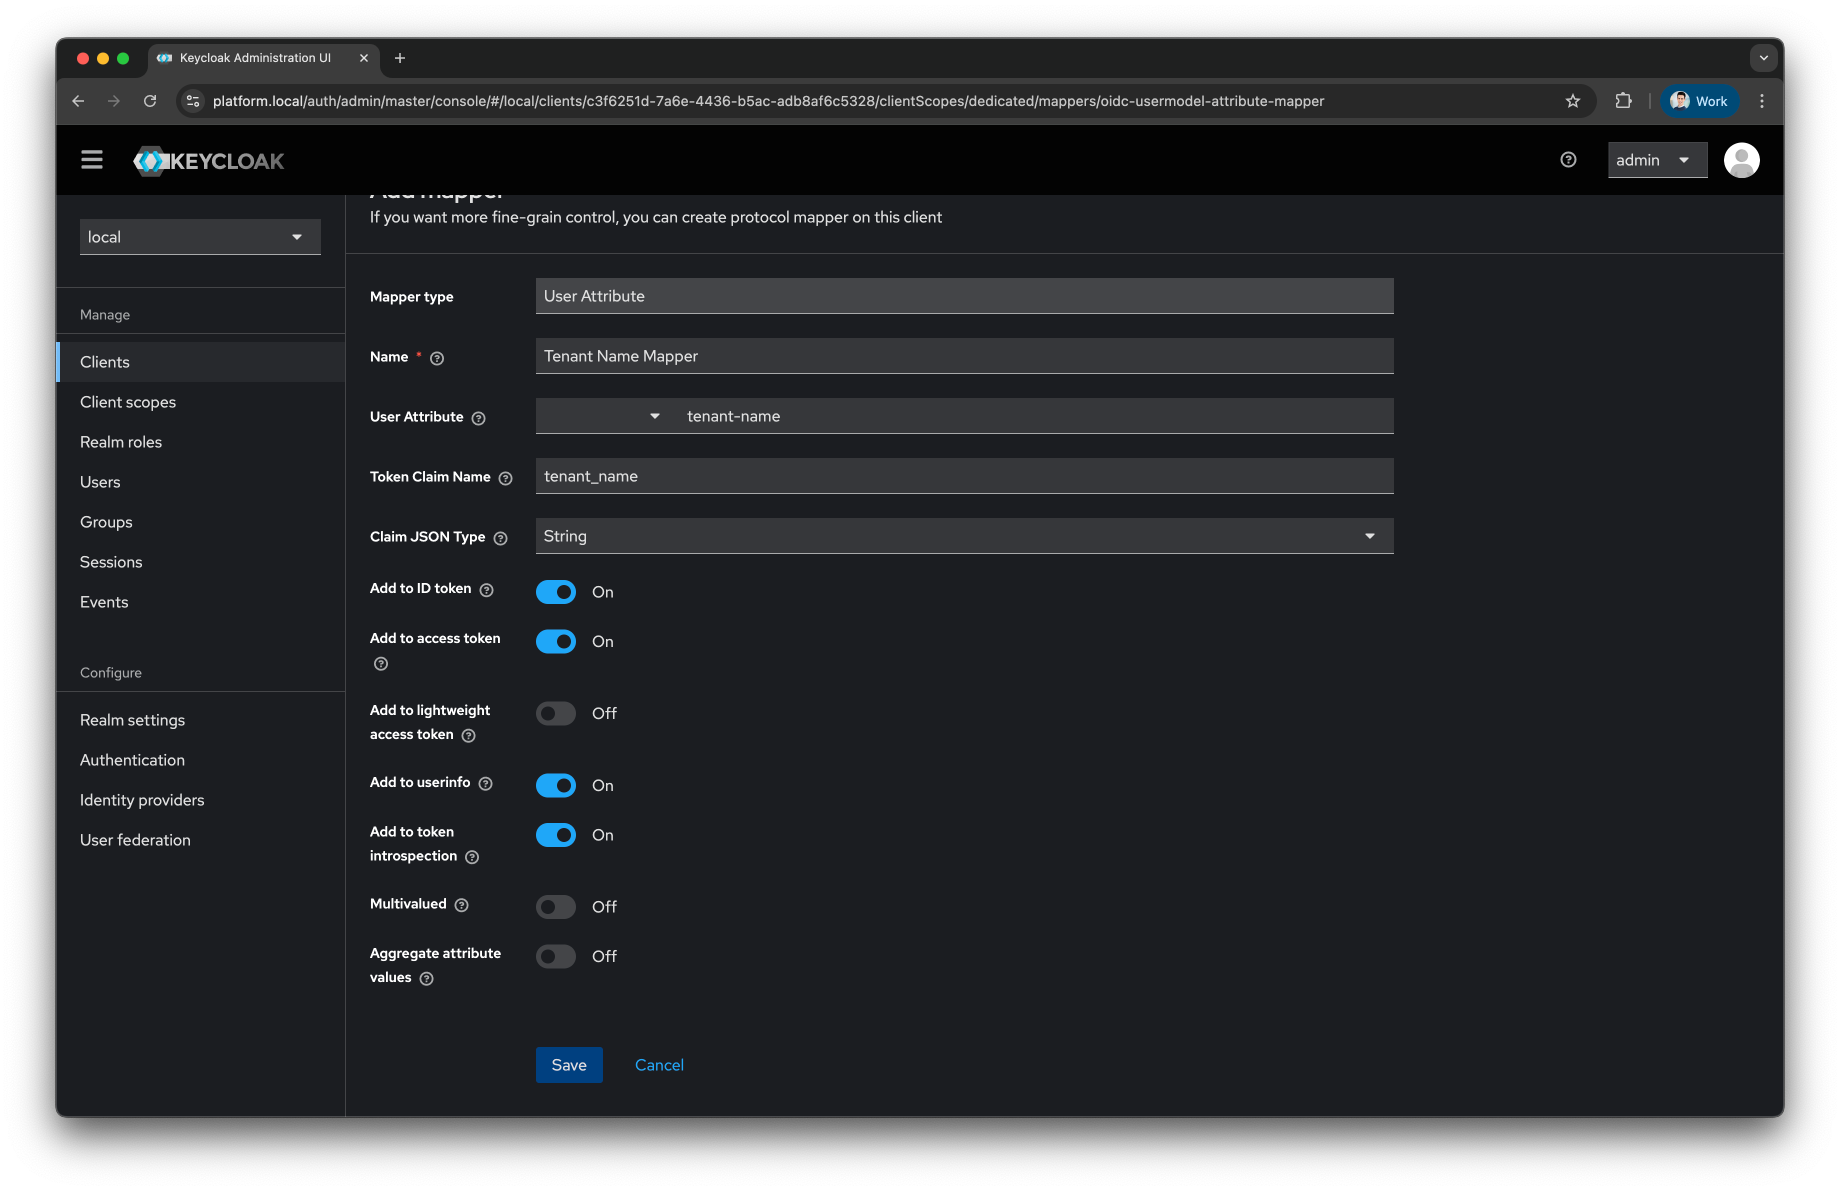
-
Press on the
self-service-dedicatedclient scope -
Press on the
Add Mapperand selectBy Configuration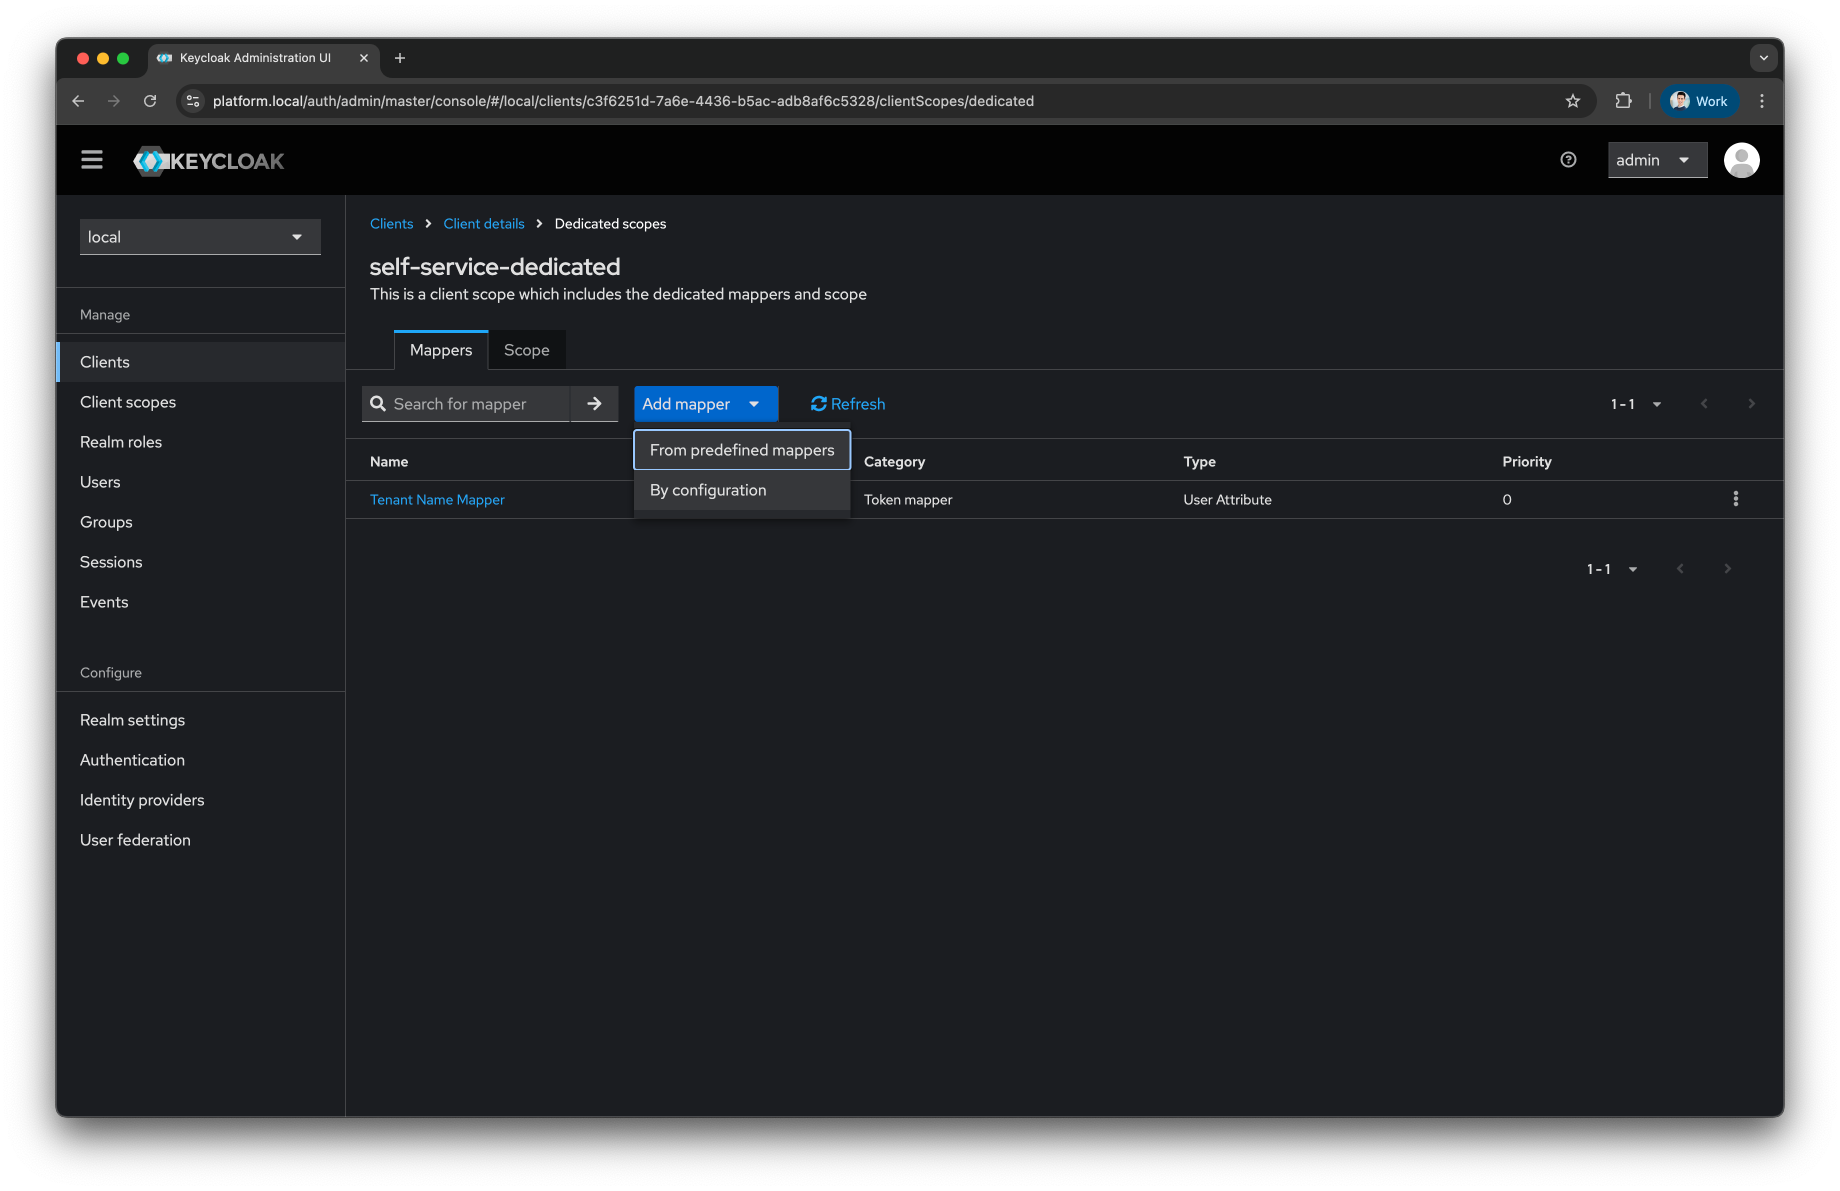
-
Select
User Attribute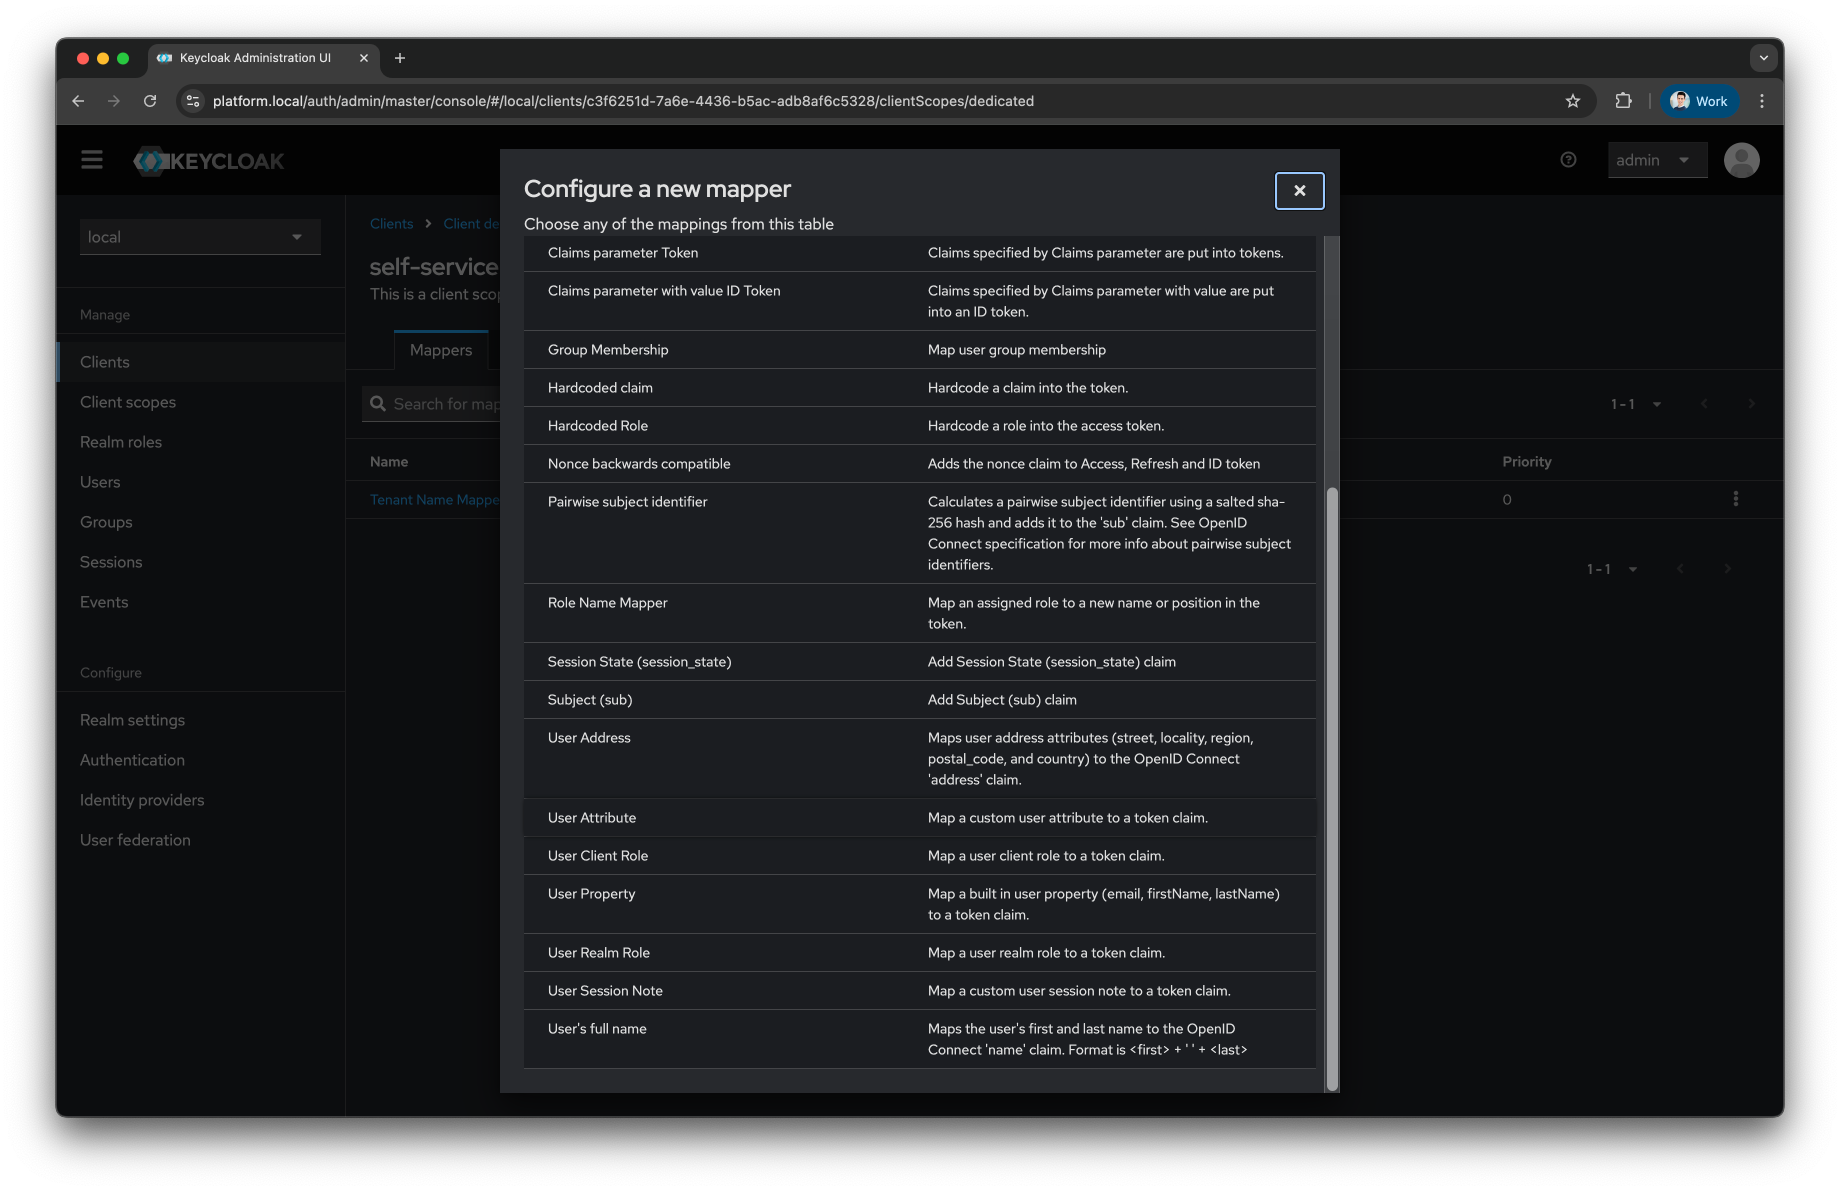
-
Fill the
Nameas Tenant Short Name Mapper -
Fill the
User Attributeas tenant-short-name -
Fill the
Token Claim Nameas tenant_short_name
-
-
Press
Savebutton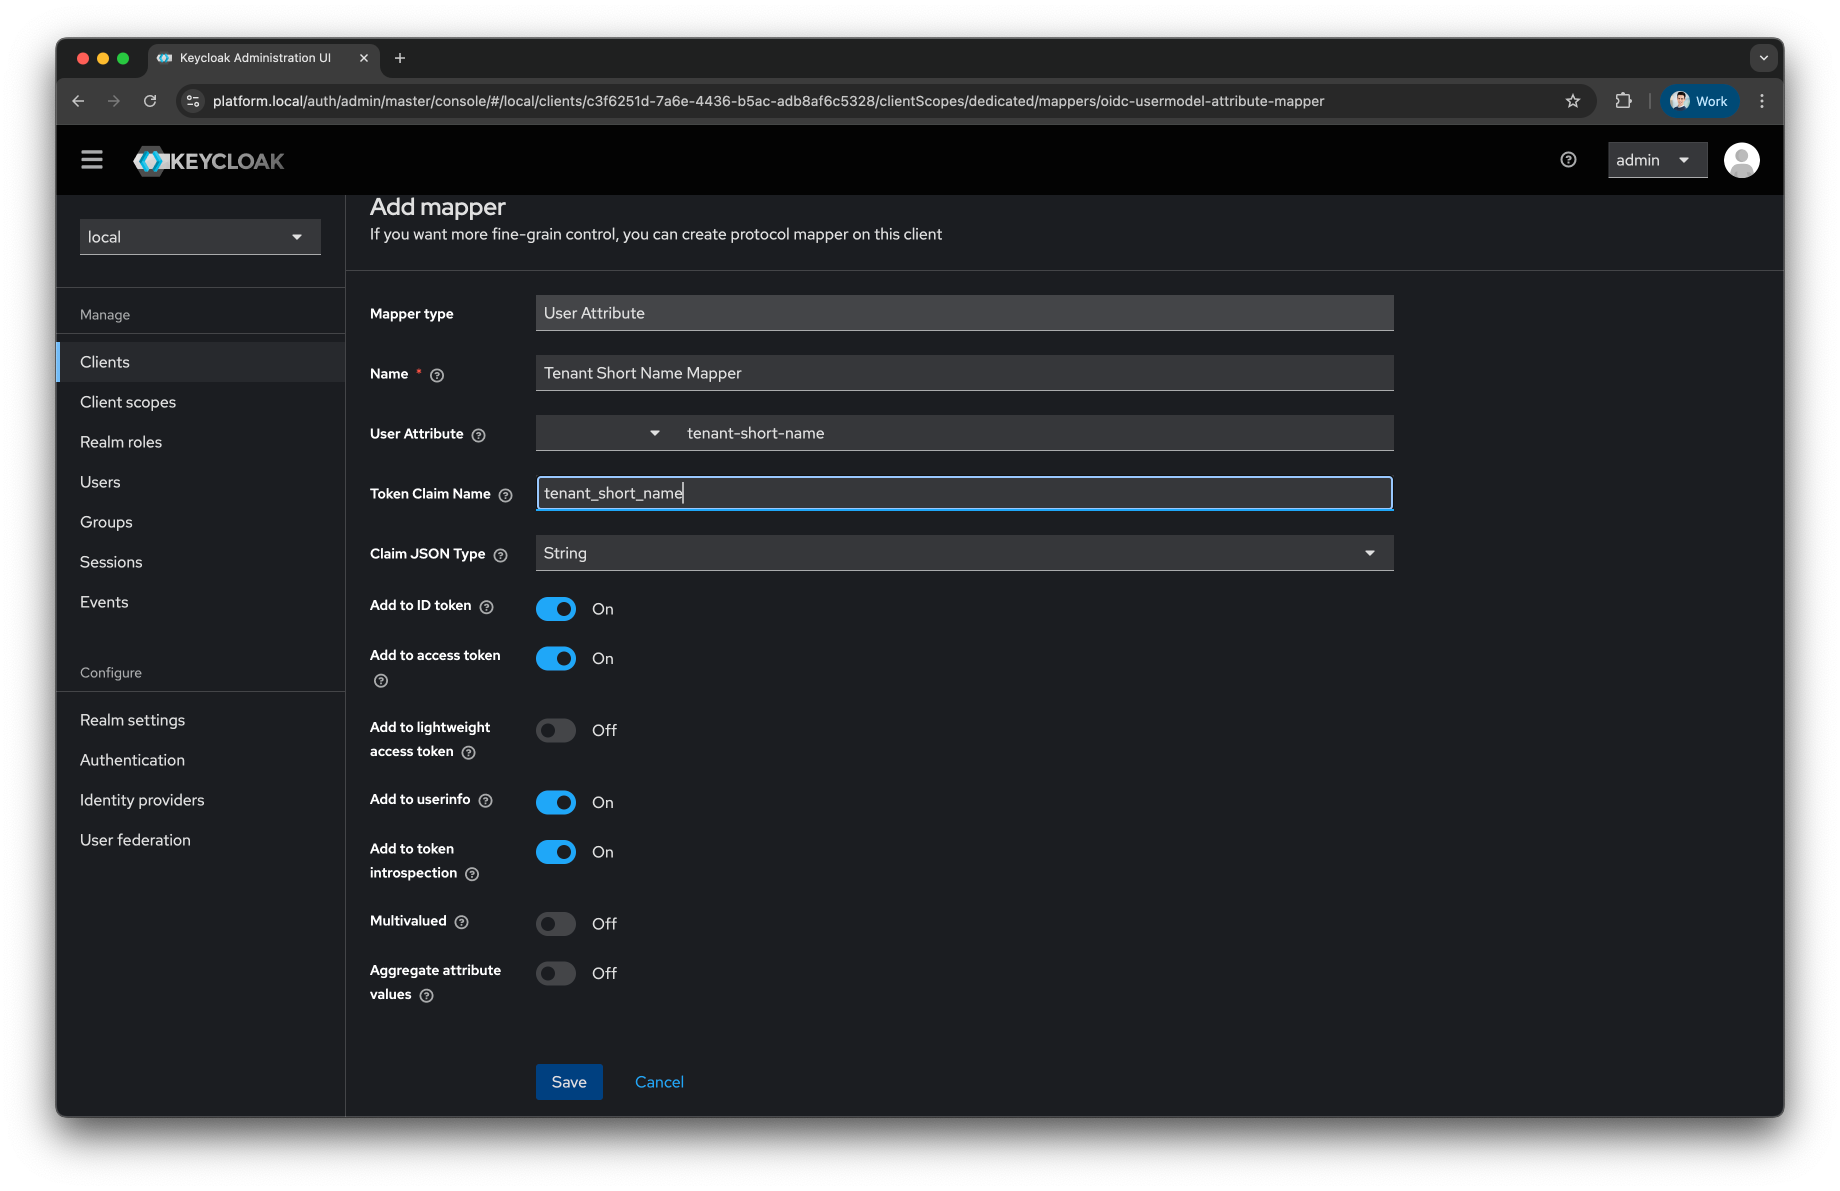
|
The Self-Service URL to access the Local Realm login screen is
or
|
Verify the local realm
Check that the client emits both tenant claims and that the realm serves the Self-Service login screen.
-
Open the
Mapperstab of theself-service-dedicatedclient scope.Expected result: the list holds both Tenant Name Mapper and Tenant Short Name Mapper. A missing mapper means Self-Service receives a token without the tenant it belongs to, so the login fails after Keycloak has already accepted the credentials.
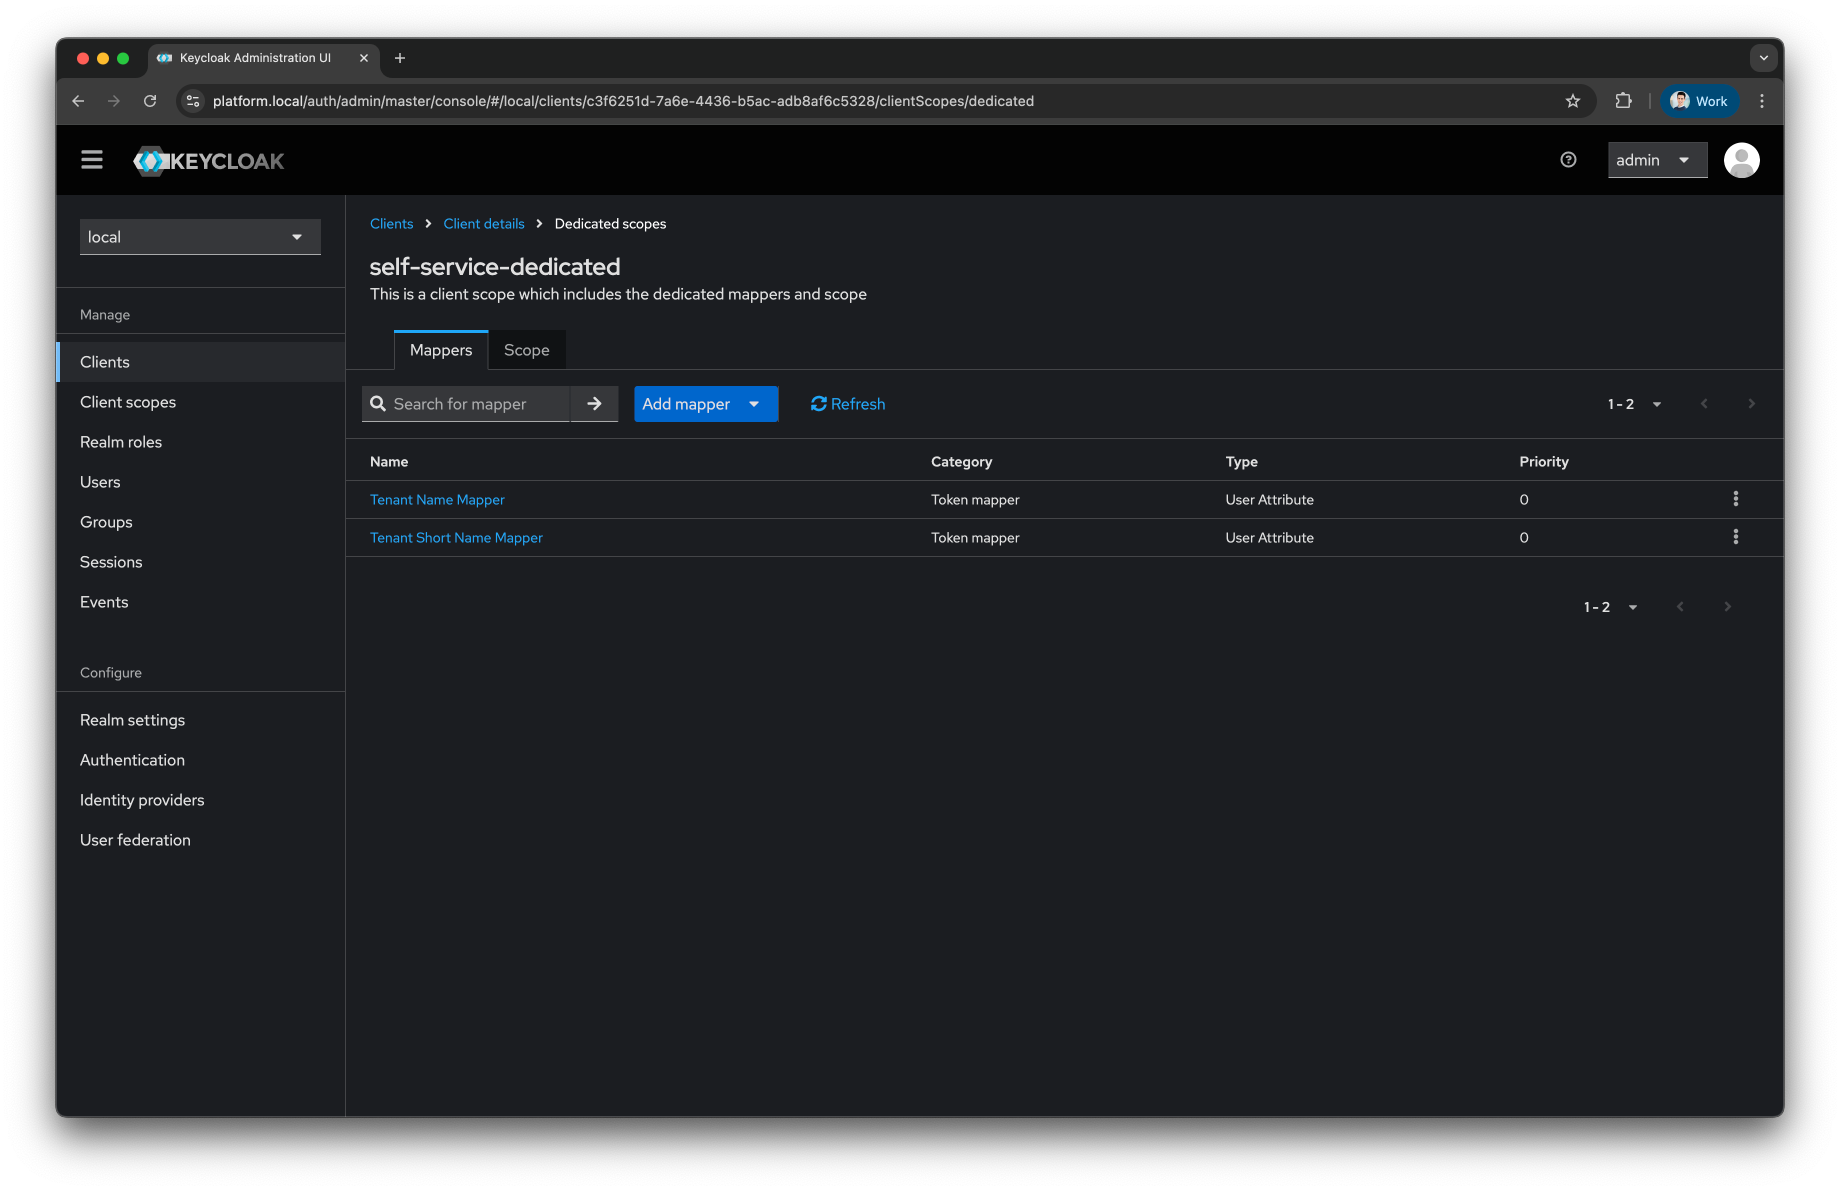
-
Open
<self-service.host>/login/localin a browser.Expected result: the login screen of the
localrealm loads and offers a registration link, becauseUser registrationis enabled on the realm. AClient not founderror instead means theClient IDis notself-service.